
Advertising cybersecurity
Advertising Cybersecurity
Expertise for Your Team
Strengthen advertiser access, protect client information, and reduce exposure across campaign platforms, tracking technologies, and creative workflows. Get practical security engineering shaped around the way your advertising team works.
A campaign connects more than an advertising account.
People approve budgets, agencies receive delegated access, tags collect events, applications exchange audience information, and creative teams share assets before launch. Each connection needs a clear owner and a controlled way to change or end access.
Nestack helps your marketing, engineering, and IT teams review these connections, prioritise security improvements, and verify agreed changes. Start with one client portfolio, campaign workflow, or application and build a practical work plan around your deadlines.
Three ways to work with Nestack
- 01
Scoped security assessment
Examine a defined advertiser portfolio, tag deployment, audience workflow, or adtech application and receive evidence-backed findings and priorities.
- 02
Dedicated security engineer
Add capacity for an agreed backlog, technical profile, working schedule, and reporting relationship with your teams.
- 03
Ongoing security improvement
Coordinate approved fixes, access reviews, retesting, recovery exercises, and updates as clients and integrations change.
Security work follows agreed authority and change procedures. Your team retains campaign, spend, publishing, and business decisions.
02Who we help
Support shaped around your role in advertising
For agencies, adtech businesses, media buying teams, and brand marketing operations worldwide. Scope reflects your platforms, clients, and the workflow you want to protect first.
Protect client workspaces, pitch material, unreleased assets, freelancers' access, and handovers between account teams.
Review advertiser-account authority, manager relationships, automation credentials, budget-change workflows, and client offboarding.
Assess tenant boundaries, campaign APIs, data pipelines, platform administration, and integration security.
Strengthen agency delegation, audience-data handling, tag publishing, brand-account recovery, and oversight of marketing suppliers.
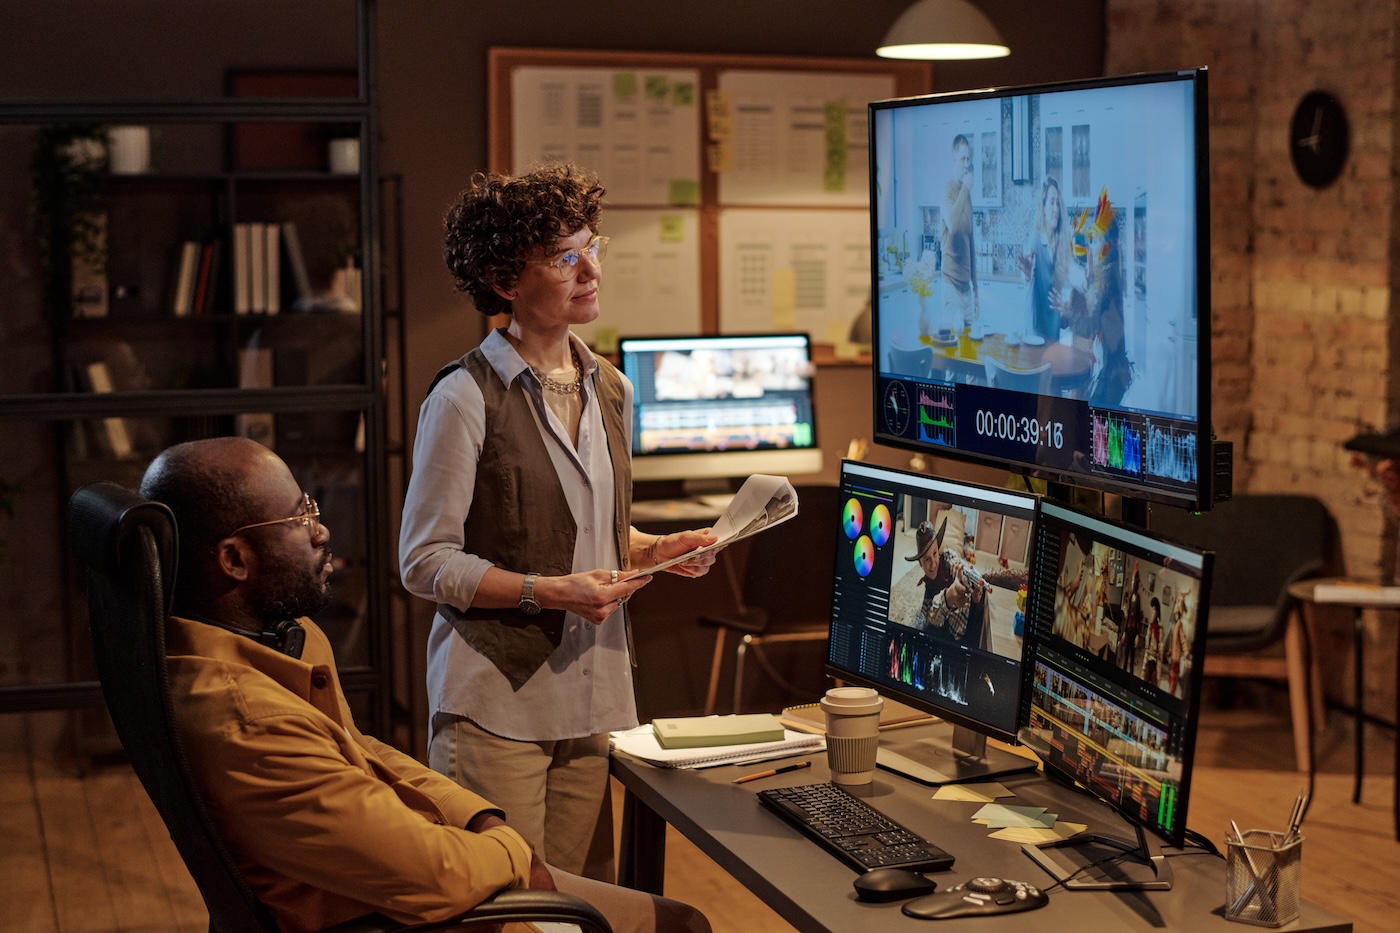
Work alongside your marketing, engineering and IT teams
We work with account leads, media operations, developers, IT and privacy owners, following your agreed authority and change procedures.
03Advertising security risk and dependency assessment
Turn a fragmented marketing stack into an actionable security plan
Security responsibilities can be scattered across the brand, agency, hosting provider, and software vendors.
We connect selected accounts and systems to the campaign activities they support, then identify the exposures that deserve attention first.
What we cover
- 01
Campaign dependencies
Advertising accounts, landing pages, identity services, asset stores, reporting tools and their owners.
- 02
Authority paths
Who can approve access, change spend, publish creative, alter destinations or connect another agency.
- 03
Client boundaries
How client portfolios, workspaces, campaign exports and shared operational tools are separated.
- 04
Integration inventory
Active connectors, automation scripts, tag containers, data transfers and their business owners.
- 05
Supplier responsibilities
Security dependencies, evidence gaps, contract-end arrangements and escalation contacts.
- 06
Prioritised remediation
Findings ranked against exposure, affected campaigns, dependencies and agreed verification criteria.
04Advertiser accounts, spend privileges, and agency access
Reduce the opportunity for unauthorised campaign and account changes
An advertising login can carry authority over valuable client relationships and active spending. We review who holds that authority, how they authenticate, and whether access ends when their assignment does.
05Tag, pixel, and marketing script security
Bring deployment discipline to code running on campaign pages
06Audience, campaign, and client-data protection
Control information as it moves between your team and partners
Audience uploads, lead exports, campaign plans, and performance reports carry different sensitivities.
We help define practical boundaries for selected datasets, then review how applications and people follow those boundaries throughout collection, activation, sharing, retention, and disposal.
What we cover
07Adtech application, API, and tenant-isolation security
Protect campaign control across applications and integrations
Advertising software may combine reporting, audience management, creative approval and campaign changes in one interface. We assess selected applications and APIs, concentrating on which customer, user and integration may perform each sensitive action.
08Creative assets, collaboration, and supplier-workspace security
Keep confidential campaign work within its intended audience
Pitch decks and unreleased creative often move through freelancers, production partners, review links and shared storage. We review these everyday collaboration routes so teams can exchange work with clearer ownership and permissions.
- 01Asset sensitivityEmbargoed launches, campaign strategy, raw footage, talent information and client-restricted material.
- 02Review and sharing linksPublic visibility, recipient limits, expiry, download settings and inherited folder permissions.
- 03External collaboratorsPartner invitations, project-limited access, review cadence and removal after delivery.
- 04Working devicesEndpoint, browser-extension, update and local-storage controls for sensitive campaign work.
- 05Content integrityApproved versions, publishing handoffs, domain administration and checks against asset substitution.
- 06Supplier assuranceProportionate evidence requests, exception tracking and handover duties for selected suppliers.
09Campaign incident readiness and operational recovery
Prepare for account compromise before a live campaign is affected
10 · Advertising AI tools and automation security
Limit what campaign assistants can read, publish, and change
AI tools can draft creative, analyse reports, and operate connected campaign systems. We review selected tools and agents against their intended job, with particular attention to confidential inputs and authority to take consequential actions.
Useful automation needs a clear boundary between recommendations and execution.
What we cover
Across the advertising lifecycle
Security priorities across the advertising lifecycle
Put security checks where campaign decisions happen. Each stage links to the service on this page that addresses it.
References reviewed October 2026Priorities for assessment, not legal advice. Consent, privacy and advertising rules differ by market, and the obligations that apply to you are confirmed with your advisers.
11Hire a dedicated advertising security engineer
Hire a Dedicated Cybersecurity Engineer
Give your advertising security backlog consistent ownership: an engineer who coordinates a defined workstream across marketing, IT and development, with the platform experience, access location, hours and specialist support agreed for your environment.
01What the engineer can own
- The agreed risk, access-review and remediation backlog
- Reviews of configurations, applications, tags or integrations
- Approved fixes with documented verification evidence
- Scoped incident exercises and client-assurance material
02How they work with your teams
- Account leads, media operations, developers, IT and privacy owners
- Named accounts, minimum access and approved environments
- Campaign calendars, change approvals and data-handling rules
- Financial, legal, creative and platform decisions escalated to owners
03How you see progress
- A prioritised plan with owners, dependencies and acceptance checks
- Regular reporting on verified fixes and remaining exposure
- Traceable access decisions, retests and approved changes
- Priorities updated as clients, platforms and automation change
One engineer is not an entire incident-response or round-the-clock monitoring team. Availability, coverage and specialist escalation are confirmed in the engagement.
12Frequently asked questions
Frequently asked questions
Showing 19 of 19 questions
The proposed services address agencies, media buying teams, adtech providers, and in-house brand operations. Confirm the platforms, workflow, technical expertise, and delivery scope during scoping.
Yes. A defined account portfolio, tag container, application, or audience workflow can provide a manageable starting point. Related systems enter scope only with appropriate authorisation.
Discuss the required platform experience, responsibilities, schedule, and reporting line. Availability and specialist support must be confirmed; software security, advertising operations, and emergency response require different skills.
Reviews can cover agreed customer-controlled settings and integrations where expertise and access are confirmed. Roles, evidence, and recovery options vary. No vendor partnership or unrestricted access is implied.
No. Authentication policies and existing integration credentials need separate review. Google's documentation, checked 25 October 2026, describes passkey enforcement rolling out to certain API users while existing refresh tokens remain unaffected by that policy. Verify the actual account and authentication workflow.
We can review privileges, approvals, automation, and available change visibility. These controls reduce exposure; they cannot guarantee prevention, spending limits across every platform, reimbursement, or recovery of losses.
Review direct and inherited access, partner relationships, application grants, shared files, and recovery ownership. Transfer required assets first, then verify removal through the appropriate account owners.
We prefer configuration reviews and isolated test environments. Any live activity requires agreed authority, prohibited actions, change windows, and stop conditions, and no testing can be promised to be entirely risk-free.
Yes, within agreed capability and scope. Reviews can examine publishing permissions, event payloads, destinations, hosting access, and change controls. Server-side collection still requires privacy and contractual review.
No. Technical tests provide evidence. Applicable law, processing purposes, consent, notices, and contracts need separate assessment. For UK activity, current ICO guidance addresses consent for advertising storage and access technologies; requirements must not be generalised worldwide.
We can assess selected access, transfers, exports, storage, client separation, and retention controls. Use synthetic records where possible and agree handling rules before sharing actual audience information.
Cybersecurity work does not certify invalid-traffic detection, viewability, attribution accuracy, brand suitability, or campaign performance. IAB seller-transparency mechanisms can support media due diligence but do not prove an account or impression is secure.
An authorised application assessment can examine tenant isolation, API permissions, integrations, and sensitive actions. Agree test accounts, synthetic data, environments, and third-party restrictions first.
Yes, where the tools and expertise are in scope. Review what each assistant reads and does, approvals for consequential actions, untrusted inputs, logging, and credential revocation.
Not automatically. Specify monitoring coverage, response hours, specialist responders, and escalation arrangements separately. Account reinstatement and other platform-controlled outcomes remain outside Nestack's control.
Agree permitted personnel and locations, customer-controlled access, confidentiality, evidence retention, and transfer arrangements. Client contracts or applicable rules may restrict access even when information stays in the customer's environment.
Agreed outputs may include ownership maps, access matrices, prioritised findings, remediation records, retests, and exercise reports. Reports distinguish observations, assumptions, and untested areas.
Scope depends on platforms, accounts, integrations, data sensitivity, testing depth, client approvals, and specialist needs. Agree milestones after discovery rather than applying a standard campaign timetable.
Describe your business, main platforms, concern, and preferred engagement. Do not submit passwords, audience lists, confidential creative, payment details, or incident evidence through the public form.
Contact and scoping call
Discuss your advertising
security priorities.
Tell us where you need support: advertiser access, campaign permissions, tags, audience data, adtech applications, creative workspaces, recovery planning, AI, or a dedicated engineer.
Loading open times…
Open times
Select an available date above to view open 45-minute times from our calendar.