
Apparel & fashion cybersecurity
Apparel & Fashion Cybersecurity
Expertise for Your Team
Protect your collection from first design to customer delivery. Strengthen security around unreleased designs, supplier collaboration, product information, and digital commerce, with practical controls shaped around sampling, production, wholesale selling, and seasonal launches.
A collection moves between designers, pattern makers, factories, sales teams, distribution partners, and digital storefronts.
Technical packs, costs, sample feedback, size information, and launch assets may travel through different systems with different owners.
Nestack helps your design, IT, sourcing, and commerce teams review these connections, prioritise improvements, and verify agreed changes. Start with the workflow that creates the most uncertainty, then build an achievable security backlog around your collection calendar.
Three ways to work with Nestack
- 01
Scoped assessment
Examine a collection workspace, supplier portal, commerce integration, or recovery scenario and receive actionable findings.
- 02
Dedicated security engineer
Add capacity with an agreed technical profile, backlog, working schedule, and reporting line.
- 03
Ongoing improvement
Coordinate approved fixes, access reviews, retests, supplier follow-up, and launch-readiness exercises.
Your owners retain design approval, production decisions, financial authority, and publication control.
02Who we help
Support for different fashion operating models
For fashion brands, apparel manufacturers, sourcing businesses, wholesalers, and direct-to-consumer teams worldwide.
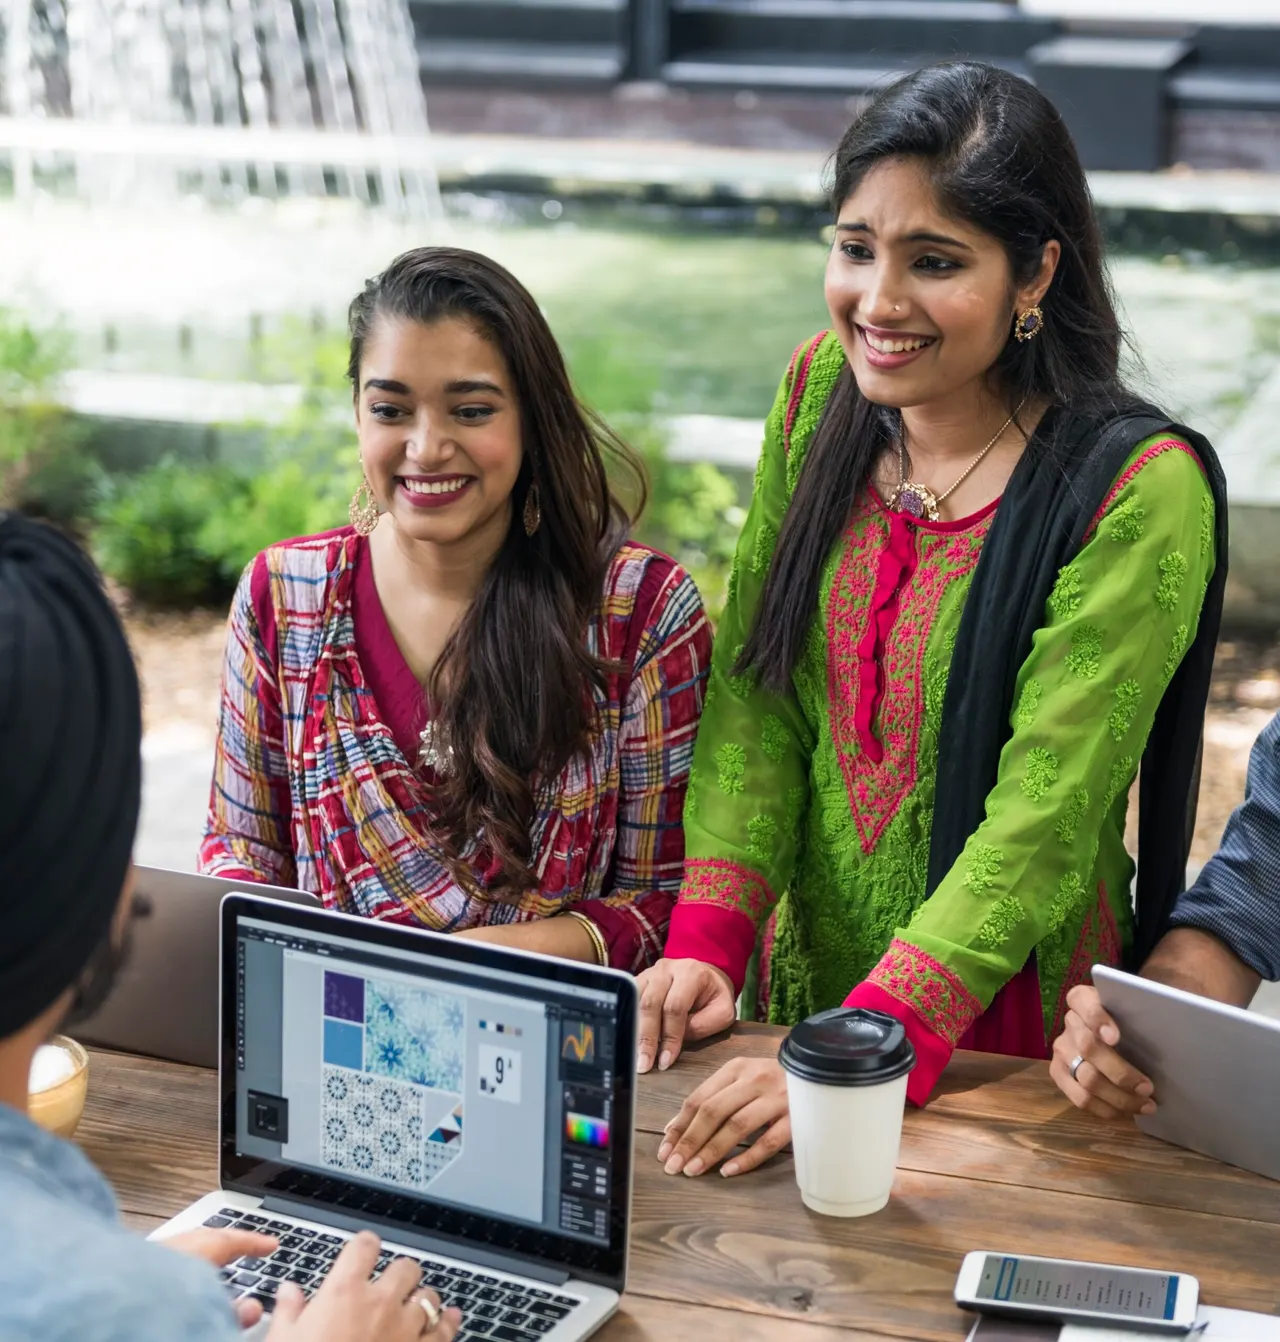
Protect unreleased collections, patterns, creative assets, pricing, and collaboration with external specialists.
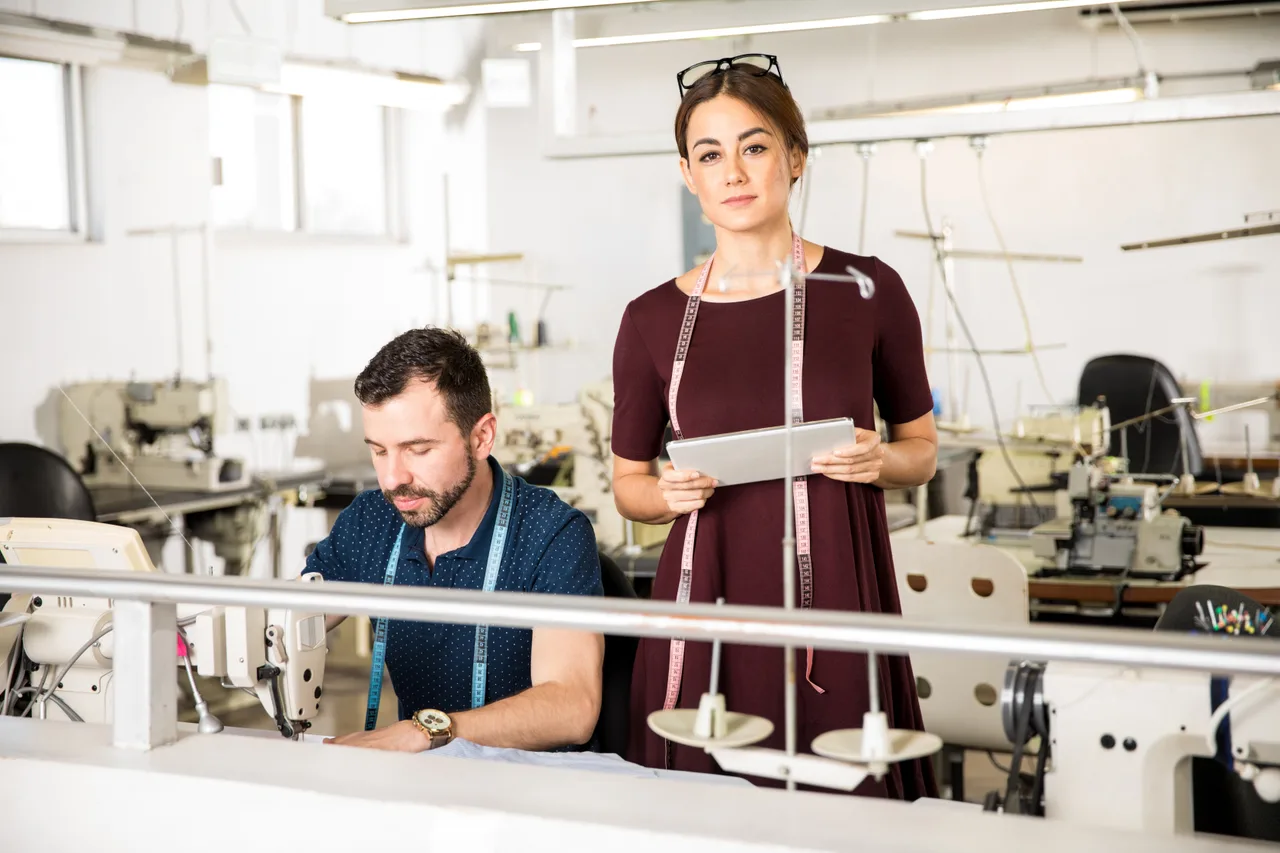
Review technical-pack exchanges, factory access, production-support systems, and customer separation.
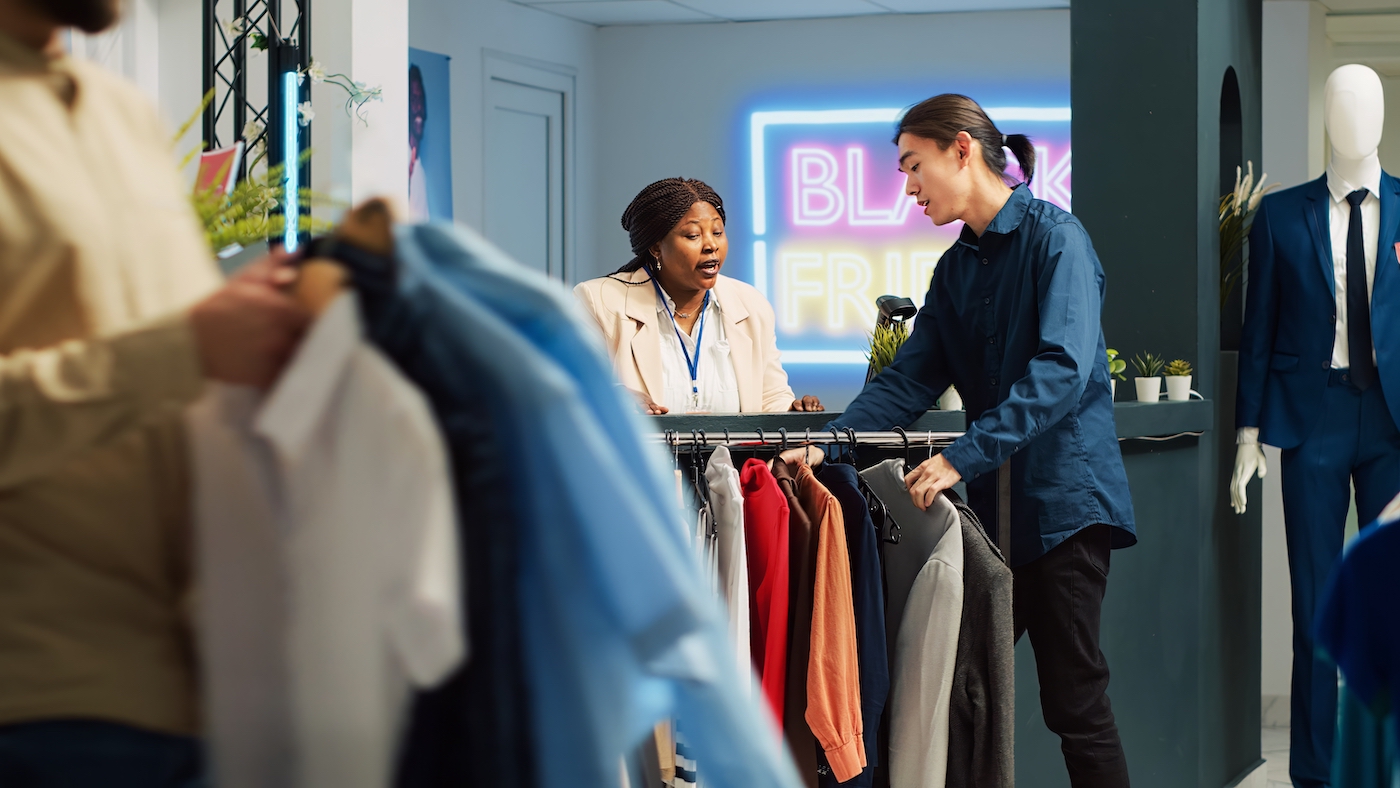
Strengthen buyer portals, line sheets, customer pricing, order integrations, and partner handovers.
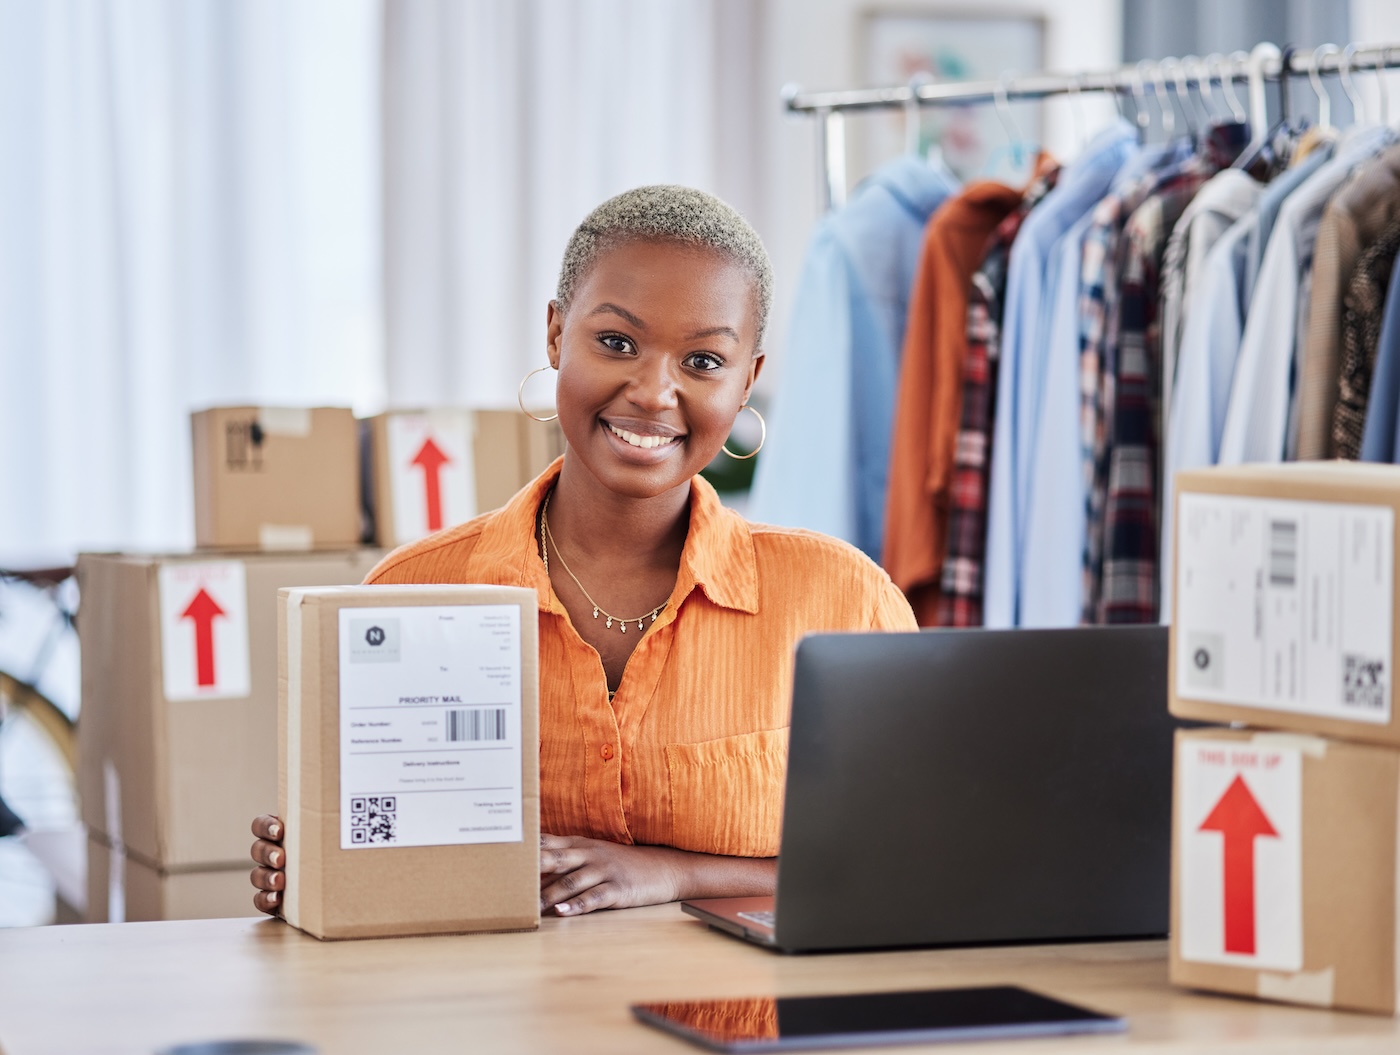
Assess store administration, apps, customer information, checkout dependencies, and limited-drop recovery arrangements.
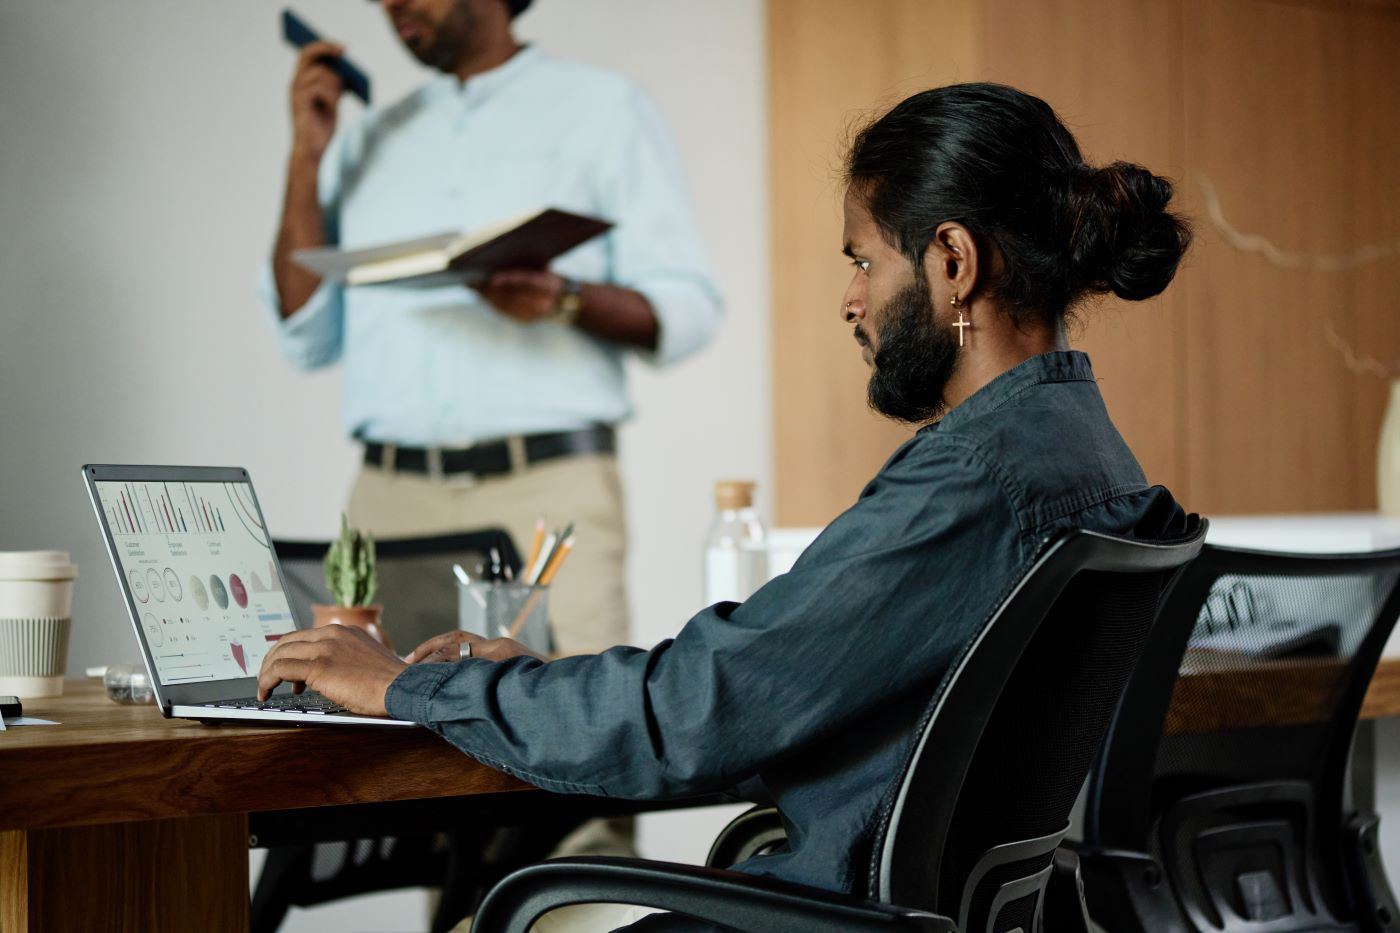
Work alongside your design, sourcing and commerce teams
We coordinate with your design, IT, sourcing and commerce owners, working around your collection calendar.
03Fashion cybersecurity risk and collection-dependency assessment
Identify the exposures that could affect a collection or launch
Security responsibilities often cross design, sourcing, production, and commerce.
We map selected systems to collection activities and identify who can view confidential information, change commercial records, or publish customer-facing content.
What we cover
- 01
Collection dependencies
Design repositories, product systems, supplier portals, order tools and store integrations, mapped to the work they support.
- 02
Information sensitivity
Unreleased designs, costs, supplier terms, customer records and embargoed imagery.
- 03
Responsibility mapping
Owners for access, release decisions, suppliers, recovery and technical changes.
- 04
External exposure
Agreed domains, sharing links, remote access and customer-controlled cloud settings.
- 05
Seasonal constraints
Sampling, production, showroom and launch windows that affect remediation.
- 06
Improvement priorities
Findings ranked by exposure, workflow impact, dependencies and verification requirements.
04Design, technical-pack, and PLM information protection
Keep unreleased collection work within its intended audience
Product lifecycle management (PLM), computer-aided design (CAD) and shared asset stores hold patterns, construction details and collection knowledge. We review selected permissions and release paths so teams can collaborate with clearer control over access and versions.
- 01Design locationsAgreed patterns, 3D files, technical packs, sample photographs and exported working copies.
- 02Collection permissionsBrand, season, product and project boundaries, including inherited folder access.
- 03External reviewSharing links, recipient restrictions, download settings, expiry and approval ownership.
- 04Version integrityChange attribution, released specifications, sample decisions and withdrawn versions.
- 05Device handlingApproved workstation access, local storage, synchronisation and supported protections.
- 06Project closureCollaborator removal, retained copies, archive permissions and agreed disposal actions.
05Supplier, factory, and freelance access security
Give each partner the access needed for its assignment
Factories, buying offices, freelance designers and development agencies need different access. We review named identities and delegated connections so permissions follow the assignment and end when the relationship changes.
06Wholesale portals, fashion applications, and API security
Protect buyer boundaries and sensitive order actions
Fashion platforms connect buyers, brands, factories and fulfilment teams. We assess selected applications and application programming interfaces (APIs), focusing on customer separation and authority over pricing, orders, product information and exports.
07Fashion commerce, checkout, and customer-data security
Reduce exposure around the store and its connected applications
08Product, inventory, and traceability-data integrity
Protect the records connecting garments with their commercial identity
Product attributes and item events connect design, factories, warehouses and sales channels.
We review selected data permissions and interfaces so unauthorised changes can be identified and approved records remain traceable across systems.
What we cover
09Collection-launch resilience and incident recovery
Prepare to restore essential work during time-sensitive periods
10 · Fashion AI tools and automated-workflow security
Limit what design and commerce assistants can access and change
AI tools can support collection research, descriptions, merchandising and customer service.
We review selected tools against their intended role, concentrating on confidential inputs and authority to take actions in connected systems.
What we cover
Across the fashion lifecycle
Security priorities across the fashion lifecycle
Put checks alongside collection decisions. Each stage links to the service on this page that addresses it.
References reviewed October 2026Priorities for assessment, not legal advice. Intellectual-property status, PCI DSS validation, privacy duties and future EU textile product-passport rules depend on the business, implementation and jurisdiction, and are confirmed with your advisers, acquirer or assessor.
11Hire a dedicated fashion cybersecurity engineer
Hire a Dedicated Cybersecurity Engineer
Give a defined fashion-security workstream consistent ownership. Agree an engineer profile suited to your applications, collaboration systems, commerce stack or supplier-access backlog, and confirm hours, approved access locations and specialist support before starting.
01What the engineer can own
- Agreed risk and remediation actions
- Reviews of selected access, integrations and configurations
- Coordinated approved fixes and retests
- Launch exercises and supplier evidence
02How they work with your teams
- Design, sourcing, IT and commerce owners
- Named accounts and approved customer environments
- Your collection calendars and change procedures
- Legal, financial and production decisions escalated
03How you see progress
- A prioritised plan with owners and dependencies
- Clear evidence of completed changes
- Reporting on unresolved exposure and exceptions
- Priorities updated as collections and partners change
One engineer does not replace equipment specialists, independent assessors or 24/7 response. Availability and coverage are confirmed in the engagement.
12Frequently asked questions
Frequently asked questions
Showing 19 of 19 questions
The proposed services address brands, apparel manufacturers, sourcing teams, wholesalers, and direct-to-consumer businesses. Confirm systems, skills, and delivery scope first.
Yes. A design workspace, supplier-access review, wholesale portal, or store integration can provide a defined starting point without assuming every business system is included.
Discuss responsibilities, platform experience, hours, and reporting. Availability and specialist escalation must be confirmed; factory equipment and commerce testing need different expertise.
Agree personnel, locations, customer-controlled access, confidentiality, and evidence handling. Contracts and applicable privacy or transfer rules may constrain remote access.
We can assess sharing, permissions, local copies, release records, and offboarding. Security work supports confidentiality but cannot guarantee secrecy or prevent every misuse.
No. Copyright, design rights, trade-secret status, ownership, and permitted reuse require separate legal assessment. Technical safeguards are one part of information protection.
We review customer-authorised access and evidence within scope. Testing a partner's own infrastructure needs that party's permission, and machinery work requires separate operational coordination.
Review accounts, shared links, app grants, integration credentials, and recovery ownership. Verify removal while retaining required assets and operational continuity.
An authorised assessment can cover collection boundaries, buyer pricing, supplier exchanges, roles, and APIs. Prefer fictional products and test accounts.
We review agreed customer-controlled settings, apps, and integrations where expertise is confirmed. Platform roles and available evidence vary; no vendor partnership is implied.
Not automatically. Responsibilities depend on the integration. PCI SAQ A's specific script eligibility criterion distinguishes embedded payment forms from redirects and fully outsourced arrangements. Confirm the applicable validation path with your acquirer or assessor.
No. This proposed service provides scoped technical findings and remediation support. Formal validation and compliance responsibilities remain with the appropriate merchant, provider, and authorised assessment process.
Yes, within agreed scope. We review access, app sharing, exports, and retention. Privacy owners determine applicable duties and approved purposes; testing uses synthetic customer records.
No. Security protects records and access. Product claims require independently supportable evidence; identifiers and protected databases alone do not establish authenticity or environmental performance.
No. As checked on 25 October 2026, the European Commission describes textile-specific requirements as forthcoming and plans delegated-act adoption for Q4 2027. That is an indicative adoption target, not a universal compliance deadline. Review final requirements and applicability before publishing legal claims.
Yes, where expertise and tools are in scope. Review confidential inputs, brand separation, connector permissions, approvals, and logging. Creative rights and content approval remain separate.
No. Agree response hours, monitoring, capacity testing, and specialist support separately. Platform outages and commercial launch outcomes cannot be guaranteed.
Platforms, partners, data sensitivity, testing depth, collection windows, and required expertise determine scope. Agree milestones and evidence-based deliverables after discovery.
Describe your business, main systems, concern, and preferred engagement. Do not send unreleased designs, customer records, credentials, payment information, or incident evidence through the public form.
Contact and scoping call
Discuss your apparel and
fashion security priorities.
Tell us where you need support: collection information, partner access, wholesale applications, commerce, product data, launch recovery, AI, or a dedicated engineer.
Loading open times…
Open times
Select an available date above to view open 45-minute times from our calendar.