
Food industry cybersecurity
Food Industry Cybersecurity
Expertise for Your Team
Protect sensitive business information. Strengthen the security of the systems connecting your food operations, customers, and suppliers. Turn security findings into a practical programme of work with clear ownership.
An order may pass through a customer portal, business application, warehouse system, supplier connection, and dispatch workflow.
Recipes, product specifications, quality records, and lot information may have different owners and access requirements. Security work needs to reflect those relationships.
Nestack helps your team identify exposure, assign responsibility, and coordinate improvements across the systems in scope. Begin with one application, a defined access problem, a recovery concern, or an agreed engineering work plan.
Three ways to work with Nestack
- 01
Dedicated cybersecurity engineer
Add a named engineer to your team for agreed priorities, working hours, and reporting, combining reviews, authorized remediation, verification, and coordination with your providers.
- 02
Scoped security assessment
Examine a specific application, identity environment, cloud configuration, or business workflow, and receive documented findings and a clearly defined route to verification.
- 03
Ongoing security support
Maintain the security backlog, review evidence, coordinate supplier follow-ups, and report progress as teams, sites, integrations, and requirements change.
A general security engagement does not authorize changes to food-processing equipment or replace food-safety, quality, engineering, or operational decision-making.
02Who we help
Security support for the businesses connecting food supply and demand
A restaurant group and a processing plant are different technical environments. We shape the work around your operations, the systems you control, and the partners you connect with.
Review business applications, recipe and specification access, production-planning interfaces, and the information supporting quality and dispatch. Coordinate with plant IT, engineering, quality, and food-safety teams where dependencies cross organizational boundaries.
Assess warehouse and transport applications, customer portals, carrier integrations, and access to shipment and temperature-history information. Clarify system ownership, service dependencies, and recovery responsibilities across partners.
Review ordering platforms, customer and loyalty information, franchise access, and connections between outlets and central systems. Establish the scope of payment-related responsibilities with the relevant provider and business owner.
Assess customer-owned food applications, APIs, mobile services, tenant boundaries, and AI-enabled workflows. Coordinate remediation with product teams and distinguish customer configuration from the underlying services supplied by other vendors.
Work with your existing specialists
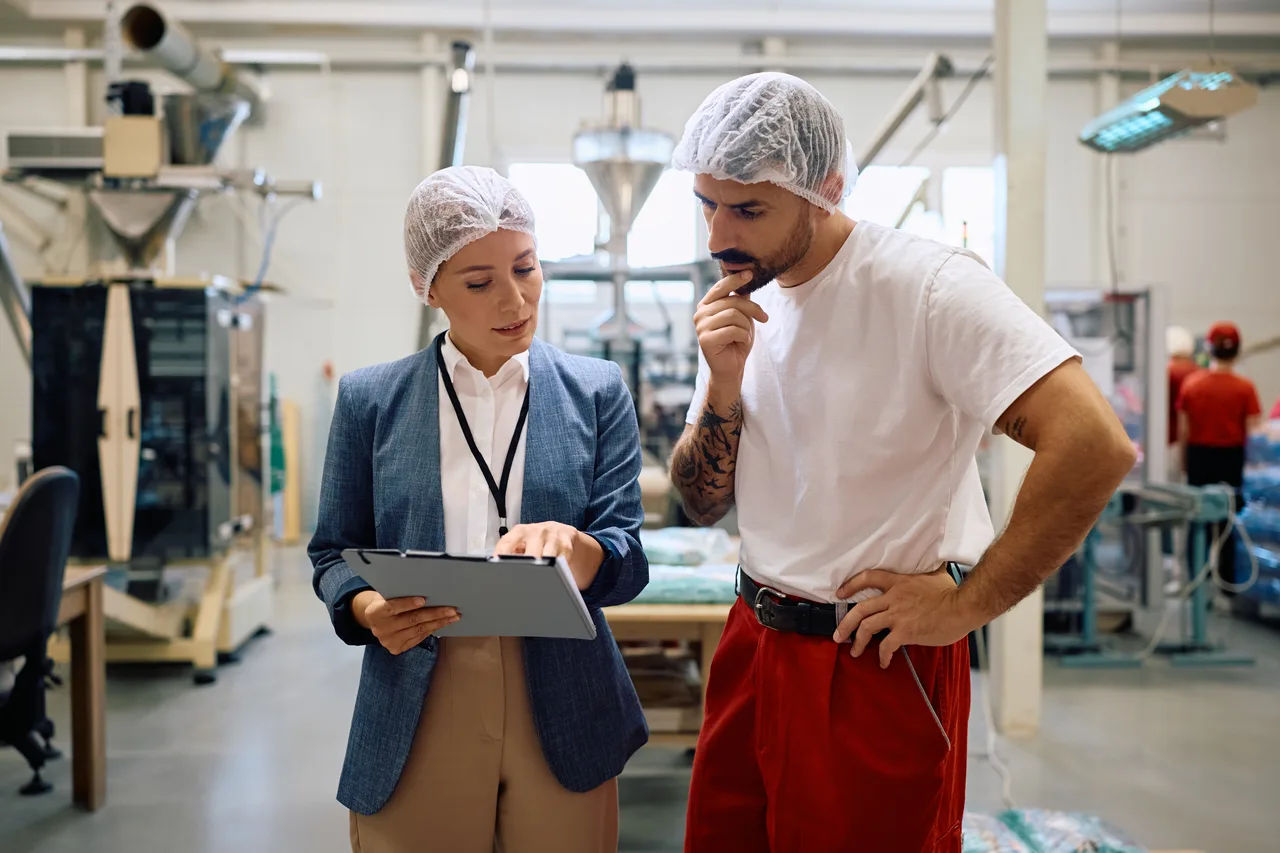
We coordinate with internal IT, managed providers, engineering, quality assurance, procurement, finance, and food-safety personnel, and agree who approves each change and who verifies its business effects.
03Food business security risk assessment
Connect security findings to the workflows your business relies on
A shared account may expose product specifications. An overlooked integration may connect an ordering portal to dispatch. A missing recovery dependency may delay access to records when they are needed.
Start by understanding the actual workflow and evidence. Nestack agrees the systems, evidence, access, and test methods, and reviews findings with the relevant owners before assigning priorities.
Assessment scope
- 01
Systems and information
Identify in-scope applications, important records, sites, integrations, and accountable owners.
- 02
People and access
Review employees, temporary staff, contractors, partners, administrators, and service identities.
- 03
Existing safeguards
Examine relevant configuration, permissions, logging, documented procedures, and prior findings.
- 04
Business dependencies
Map how information moves between order capture, planning, quality, warehousing, and dispatch.
- 05
Priorities and ownership
Connect observed weaknesses to agreed business impact, practical actions, and decision-makers.
01Departed contractor retains portal access
Evidence to examine:Account and assignment records
Possible consequence:Continued access to supplier information
Recommended action:Confirm owner; remove or adjust access
Proposed owner:Portal owner
02Broad recipe-document permissions
Evidence to examine:Group membership and share settings
Possible consequence:Unnecessary disclosure or editing
Recommended action:Define roles and review access
Proposed owner:Product information owner
03Integration account has excess rights
Evidence to examine:API configuration and permitted operations
Possible consequence:Unapproved changes to business records
Recommended action:Narrow permissions and verify workflow
Proposed owner:Application owner
04Restore test excludes dispatch dependencies
Evidence to examine:Backup scope and exercise records
Possible consequence:Incomplete business-system recovery
Recommended action:Map dependencies; rehearse agreed scenario
Proposed owner:IT recovery owner
05Assistant retrieves across customer accounts
Evidence to examine:Test users and retrieval results
Possible consequence:Exposure of another customer's information
Recommended action:Enforce access boundaries and retest
Proposed owner:Platform owner
These fictional examples demonstrate report structure. They are not findings about a Nestack customer. Actual severity depends on the assessed environment.
04Application, API, and traceability-data security
Review the boundaries around your applications and business records
We assess who can read, change, export or transmit information in your customer-owned ordering, warehouse, supplier and traceability applications. Testing your configuration does not authorize probing a SaaS provider's platform.
05Cloud, site IT, and connected-system security
Strengthen the environments connecting offices, sites, and partners
06Identity, workforce, and partner access
Keep access aligned with people's current responsibilities
Permanent staff, seasonal workers, contractors, franchise teams and equipment suppliers need different permissions. We make them reviewable and accountable.
07Ransomware and business recovery readiness
Prepare to restore information and coordinate business decisions
08Security governance and customer assurance
Show customers how security responsibilities are managed
Customer contracts, supplier reviews, insurance requests, and internal policies may call for different evidence. Organize that evidence around the actual scope of the business and the requirements that apply.
Food-safety programmes and security assurance have different purposes. Security engineering does not itself award food-safety certification or certify regulatory compliance.
What the engagement can cover
09Supplier, logistics, and third-party security
Review the access and dependencies introduced by partners
We focus each review on what an ingredient supplier, contract manufacturer, carrier, warehouse provider or digital service can access, and what your business depends on.
- 01Supplier classificationThe information, access, services and business dependencies a relationship introduces.
- 02Evidence reviewRelevant assurance material, its scope, dates, limitations and unanswered questions.
- 03Data exchangeApproved sharing methods, portal permissions, integration identities and onward access.
- 04Remote supportThe approved route, users, session scope and access-removal arrangements.
- 05Incident and continuity coordinationContacts, notifications, recovery dependencies and participation in exercises.
- 06Relationship changes and exitAccess removal, information return or deletion, and responsibilities when providers change.
10 · Food business AI and agent security
Control the information and actions available to your assistants
An assistant may retrieve supplier documents, summarize customer enquiries, draft procurement requests, or help staff find product information. Its access and permitted actions need a defined scope.
Security testing does not validate allergen advice, food-safety instructions, recipes, shelf-life decisions, or autonomous process control. Appropriate business and specialist review remains necessary.
What the review can cover
Across the food supply chain
Security priorities across the food supply chain
Eight areas to examine as systems, sites, and relationships change. Each is an assessment priority rather than a new legal requirement, with the service that addresses it.
References reviewed October 2026Priorities for assessment, not legal advice. Duties depend on the products, activities, contracts, and markets involved and are confirmed during scoping.
11Hire a dedicated food industry cybersecurity engineer
Hire a Dedicated Cybersecurity Engineer
One consistent engineer who owns an agreed security work plan alongside your IT, application teams and suppliers, working remotely from India through customer-approved access.
01The engineer owns
- Security backlog and evidence register
- Access, configuration and application reviews
- Approved remediation and verification
- Supplier follow-ups and dependencies
- Reporting on work, findings and decisions
02You decide
- Business priorities, access and risk
- Production, equipment and payment changes
- Food safety, quality and product release
- Legal, contractual and external communication
03Agreed up front
- Role, supervision and working hours
- Delivery location, access and tools
- Deliverables, reporting and escalation
- Leave cover and specialist support
Full-time means an agreed schedule; it does not imply 24/7 monitoring or emergency response. Physical work and operational changes may need local personnel or specialist partners.
12Frequently asked questions
Frequently asked questions
Showing 19 of 19 questions
Yes. Review the proposed role, relevant experience, and technical approach before confirming the engagement. Confirm availability, oversight, schedule, and commercial terms together.
Yes. Define the responsibilities of internal IT, managed providers, quality, food safety, engineering, and business owners. Technical security support should fit the customer's approval and escalation processes.
Yes. A defined application, access review, or recovery scenario can provide a practical starting point. Record dependencies that require wider participation rather than assuming a single system operates independently.
Scope may include customer-owned ordering applications, business platforms, warehouse interfaces, supplier portals, traceability-data exchanges, identity, and cloud environments. Confirm each target, method, permission, and exclusion before work begins.
Only within that provider's authorization and rules. Reviewing your own tenant configuration or permitted integration is different from testing the vendor's underlying infrastructure.
We can review relevant access, application behavior, sharing, and change evidence within scope. Your product, quality, and food-safety owners remain responsible for whether the information itself is correct and suitable for its intended use.
Not by default. Production controls, refrigeration equipment, packaging machinery, and safety systems require separate scope, appropriate expertise, and operational authorization. Business IT access does not provide permission to change equipment.
Yes, subject to agreed capabilities and scope. Review ordering, customer data, outlet access, and relevant payment responsibilities. Any formal payment-security assessment or validation service must be explicitly confirmed with the appropriate qualified parties.
Agree test windows, accounts, methods, rate limits, stop conditions, and business contacts. Use evidence review and controlled test environments where appropriate. Do not treat live scanning or system changes as automatically permitted.
Your designated operational, quality, and food-safety authorities decide. Restoring software or passing a security retest does not establish that equipment is safe, food is suitable, or business records are complete.
Where suitable, work can use customer-controlled environments and approved access. Confirm hosting, personnel locations, logging, recordings, downloads, retention, and handling of recipes and customer data before delivery begins.
Establish restrictions before onboarding. Consider redacted evidence or customer-operated checks where these can meet the objective. If restrictions prevent effective delivery, state the limitation and agree an appropriate alternative arrangement.
Security work can support technical controls and evidence; it does not automatically establish compliance or award food-safety certification. Applicable duties depend on the products, activities, contracts, and markets. Confirm interpretation with qualified advisers.
No. A dedicated engineer has an agreed schedule. Continuous monitoring, out-of-hours response, specialist escalation, and leave cover must be defined separately where available.
The proposal defines what is included. An assessment may provide recommendations only, while an engineering engagement may include approved implementation and verification. Identify responsibilities and completion evidence before work starts.
Availability is not implied by this page or a general engineering assignment. Confirm emergency-response contacts, coverage, and specialist capability in advance. Use established incident arrangements for urgent situations.
Use approved tools and information-handling rules. Restrict recipes, credentials, customer data, and sensitive supplier content to authorized workflows. Prefer representative synthetic or approved data for testing where practical.
No. Testing access, information exposure, and connected actions does not validate the factual or scientific accuracy of advice. Food-safety and quality decisions require the appropriate expertise, review, and approval.
Scope, complexity, access restrictions, available evidence, delivery locations, and implementation responsibilities determine the proposal. Agree deliverables, acceptance evidence, reporting, knowledge transfer, and access removal at the outset.
Contact and scoping call
Tell us where your food business
needs security support.
Start with your current priorities and the systems involved: a dedicated engineer, one application or access concern, or recovery and supplier assurance.
Loading open times…
Open times
Select an available date above to view open 45-minute times from our calendar.