
Accounting cybersecurity
Accounting Cybersecurity
Expertise for Your Team
Protect confidential client records. Strengthen access to accounting, tax, and payroll systems. Reduce exposure to email-led fraud and prepare your firm for disruption with security work that has clear owners and measurable follow-through.
Your team handles information that can expose much more than an account balance.
Identity documents, tax records, payroll details, bank instructions, business plans, and audit evidence move through email, client portals, cloud applications, spreadsheets, and external service providers.
Nestack helps you examine the controls around those workflows and turn findings into a practical programme of improvement. Start with a defined security concern or discuss a dedicated engineer who works with your practice leaders, IT team, and service providers.
Three ways to work with Nestack
- 01
Scoped assessment
Review an agreed environment or workflow and receive prioritised findings, evidence, and a remediation plan.
- 02
Dedicated security engineer
Add engineering capacity with an agreed technical profile, schedule, reporting line, and work backlog.
- 03
Ongoing improvement
Coordinate access reviews, configuration changes, remediation, retesting, and updates to security evidence.
Security support for accounting practices, tax firms, outsourced finance providers, and in-house finance teams.
02Who we help
Security support across accounting and finance services
Scope is tailored to your role, systems, client commitments, and the markets in which you operate.
Protect client workspaces, engagement files, audit evidence, partner accounts, and confidential transactions across teams and offices.
Improve controls around taxpayer records, client uploads, filing access, seasonal staff, and deadlines.
Review client separation, payroll access, bank-detail changes, file transfers, and service continuity across multiple customers.
Strengthen access and security around financial reporting, receivables, payables, expense systems, and external accountants.
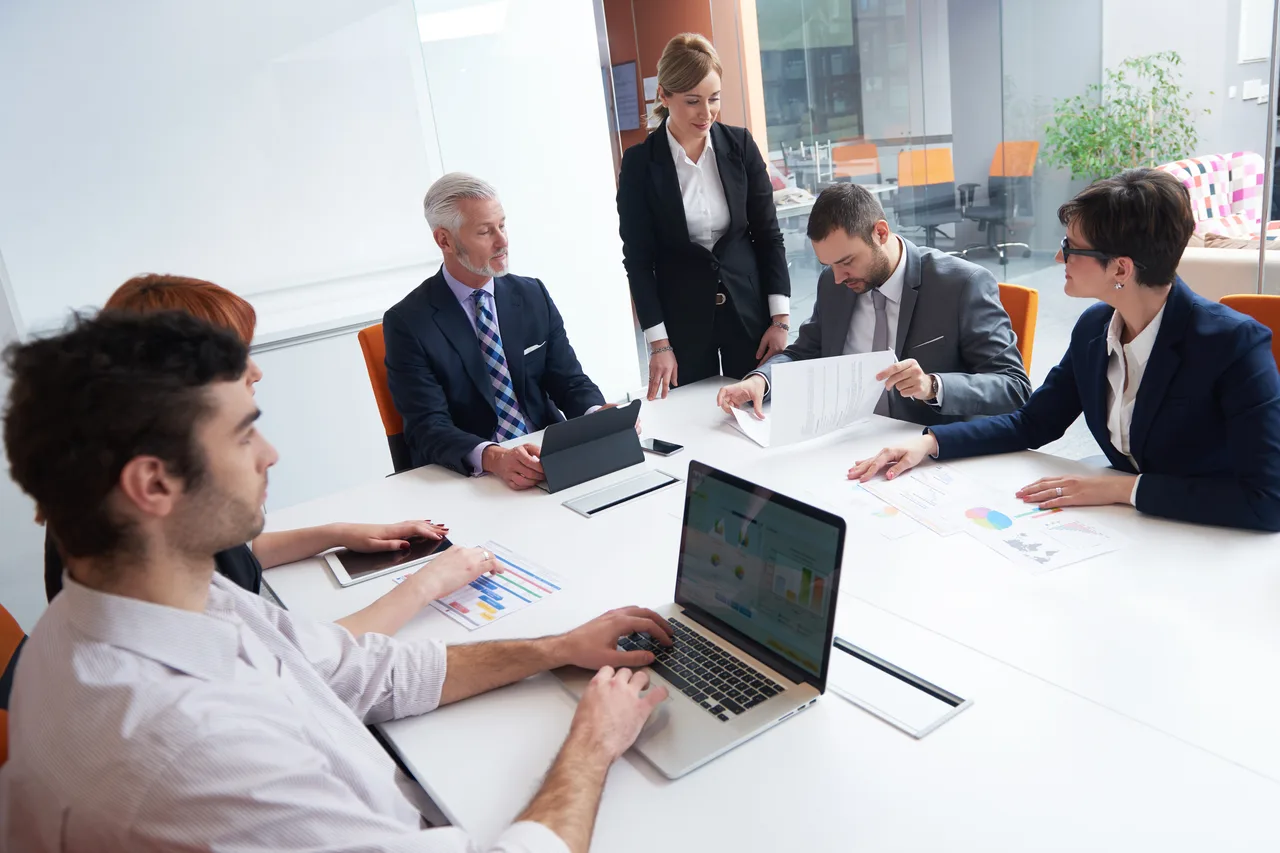
Work alongside your IT team and providers
We complement your existing IT team or provider, with responsibilities for administration, security changes, alerts, backups and escalation agreed so nothing is assumed or duplicated.
03Accounting security risk assessment
Know where your firm's most important exposures are
A useful assessment connects technical findings to the work your firm must protect.
We review selected systems, people, suppliers, and information flows to identify where client confidentiality or operational continuity could be affected.
What we cover
- 01
Systems and data
Agreed accounting, tax, payroll, document and collaboration systems, and their owners.
- 02
Client information flows
How records are collected, shared, exported, retained and removed.
- 03
Workflow risks
Onboarding, document requests, bank-detail changes, filing preparation and offboarding.
- 04
Existing controls
Selected access, email, device, backup and logging arrangements against the agreed baseline.
- 05
Supplier dependencies
Reliance on software vendors, IT providers, subcontractors and specialist processors.
- 06
Remediation priorities
Findings ranked by exposure, business effect, effort and dependencies, with accountable owners.
04Email, phishing, and payment-workflow security
Strengthen the controls around trusted communications
A familiar-looking email can lead to a malicious attachment, a stolen account or a changed payment instruction. We help your IT and finance owners improve the technical protections and the verification steps around them.
05Identity, client separation, and privileged access
Give people the access they need, for the work they are assigned
Partners, engagement teams, temporary staff, client users and external specialists all need access. We review how it is granted, checked and removed, keeping clients and responsibilities separate.
06Cloud accounting, collaboration, and endpoint security
Strengthen the environments your team uses every day
07Client portal, application, and API security
Check whether sensitive records stay within their intended boundaries
Client portals and integrations can move large amounts of information between bookkeeping, payroll, tax, document, and reporting systems.
We assess selected applications and interfaces under an agreed, authorised test plan, preferring non-production systems and synthetic records. Real payments, tax submissions and live client records are never used as ordinary security tests.
What we cover
08Ransomware readiness and operational recovery
Prepare to recover the work that cannot wait
09Client data protection and supplier assurance
Make confidentiality controls easier to explain and maintain
Client information passes through people, systems and external organisations. We document those relationships and improve the controls behind your security commitments.
- 01Data handlingSensitive record categories and approved collection, storage and sharing methods.
- 02Retention and disposalOwner-approved schedules turned into technical settings, with exceptions and legal holds.
- 03Information security plansDocumented policies, responsibilities, risk treatment and periodic review.
- 04Supplier assessmentSecurity evidence, access arrangements, incident contacts and subcontractor dependencies.
- 05Delivery and access boundariesAuthorised locations, accounts, export restrictions and cross-border access considerations.
- 06Evidence managementControl records kept current, and accurate answers to security questionnaires.
10 · AI and automation security for accounting
Keep sensitive information and financial actions under control
AI assistants and automation can help extract invoices, search documents, draft responses, and prepare reconciliations. Their access to records and tools needs deliberate limits, especially when an output could influence a client decision or a financial transaction.
Security testing does not establish accounting accuracy or tax correctness. Qualified business owners retain responsibility for financial judgement, evidence review, postings, and submissions.
What we cover
Across the client lifecycle
Security priorities across the client lifecycle
Build protection into the work, from onboarding to closure. Each stage links to the service on this page that addresses it.
References reviewed October 2026Priorities for assessment, not legal or regulatory advice. Obligations differ by market and activity and are confirmed with your advisers during scoping.
11Hire a dedicated accounting cybersecurity engineer
Hire a Dedicated Cybersecurity Engineer
Give agreed security work a named owner who collaborates with your team, explains findings, coordinates changes and shows progress, with the role defined around your environment and priorities.
01What the engineer can own
- An agreed risk and remediation backlog
- Configuration, access and event reviews
- Approved hardening, retests and evidence
- Access reviews, exercises and recovery tests
02How they work with your team
- Practice leaders, IT and process owners
- Named accounts and least-privilege access
- Your change, escalation and evidence processes
- Agreed coverage hours and handover
03How you see progress
- A prioritised plan with accountable owners
- Status reports and unresolved dependencies
- Evidence of completed changes and retests
- Periodic review of remaining exposure
Specialist testing, legal advice, incident forensics and continuous monitoring may need additional roles or separate services. Your firm keeps business approvals and risk acceptance.
12Frequently asked questions
Frequently asked questions
Showing 19 of 19 questions
The proposed service covers accounting and audit practices, tax and bookkeeping firms, payroll providers, outsourced finance teams, and internal finance departments. Scope depends on your environment and requirements.
Yes. A defined email, access, portal, cloud configuration, recovery, or AI review can provide a practical starting point. Agree systems, deliverables, and permissions before work begins.
Discuss a dedicated engagement with a defined skill profile, schedule, backlog, and reporting line. Confirm availability and any specialist support during scoping.
The work can complement your existing IT team or provider. Set responsibilities for administration, security changes, alerts, backups, and escalation so tasks are not assumed or duplicated.
We first confirm the product, hosting model, subscription features, integrations, and available permissions. Customer-configuration work differs from testing a vendor's platform, which may require separate authorisation.
Controls can reduce exposure, but no service can guarantee prevention. Effective work combines email and identity controls with independent verification, approval separation, training, and incident escalation.
Yes, through agreed role design, access expiry, onboarding and offboarding checks, and periodic reviews. Your managers approve who needs access to each engagement.
Testing is planned around operational constraints. Prefer non-production environments and synthetic data, with agreed test windows and stop conditions. Real payments and submissions are excluded unless separately and explicitly authorised.
Do not assume these are part of a dedicated engineer engagement. Coverage, alert handling, emergency response, specialist support, and service commitments must be separately agreed.
We can review the agreed coverage and supported recovery options. Vendor availability, retention, export, and backup features are different capabilities; confirm them and test relevant restore procedures.
Work can be designed around customer-controlled environments, limited downloads, and sanitised evidence. Remote access and support logs still need review for contractual, privacy, and cross-border requirements.
Agree the authorised delivery locations, named personnel, access methods, overlap hours, escalation route, and data-handling rules before access starts. Local or onsite activity requires a separately agreed arrangement.
We can support scoped policy and security-plan work tied to actual controls and owners. For example, written information security plan requirements may apply to US tax-preparation activities. Confirm applicability with your advisers; this is not a universal rule for all accounting businesses.
The service can support control improvements and evidence preparation. It does not itself confer a certification, audit opinion, or legal compliance status.
Yes, within an agreed technical scope covering data access, disclosure, untrusted instructions, tool permissions, and approval controls. Accounting accuracy and professional judgement need separate evaluation.
Agreed deliverables may include prioritised findings, owner-assigned actions, remediation records, retest evidence, and concise progress reports. Define the reporting format at the start.
Pricing depends on systems, scope, complexity, access arrangements, coverage, and specialist needs. Scope the work before agreeing a project fee or engineering engagement.
Timing depends on access, testing permissions, dependencies, and your operational calendar. Agree milestones after scoping rather than relying on a standard timeline.
Share your organisation type, approximate environment, main concern, and desired engagement. Do not upload client records, bank details, identity documents, or credentials through the public enquiry form.
Contact and scoping call
Discuss your accounting
security priorities.
Tell us where you need support: protecting client records, reviewing access, improving email security, assessing an application, preparing for disruption, or adding a dedicated engineer.
Loading open times…
Open times
Select an available date above to view open 45-minute times from our calendar.