
Aerospace & defense cybersecurity
Aerospace & Defense Cybersecurity
Expertise for Your Team
Protect engineering information and the systems behind programme delivery. Build a practical improvement plan across technical data, supplier access, software, manufacturing, and maintenance, with clear owners and evidence of completed work.
A drawing, software package, inspection result, or maintenance record may pass through several organisations before it supports a delivery decision.
The security question includes who can view that information, who can change it, and whether the receiving team can identify its approved source and version.
Nestack helps your IT, engineering, quality, and operations teams assess selected systems, implement approved improvements, and organise technical evidence. Start with an eligible business environment or a clearly defined workflow, and expand only when responsibilities, permissions, and delivery requirements are understood.
Three ways to work with Nestack
- 01
Scoped security assessment
Review an agreed engineering workspace, supplier connection, application, build environment, or recovery scenario and receive prioritised findings.
- 02
Dedicated security engineer
Add capacity with an agreed technical profile, work backlog, reporting line, access eligibility, and delivery schedule.
- 03
Ongoing security improvement
Coordinate approved changes, access reviews, retesting, exercises, and evidence updates as programmes and suppliers evolve.
Your responsible teams retain engineering approval, risk acceptance, regulatory decisions, and operational control.
02Who we help
Security support for distinct aerospace and defence responsibilities
For civil aerospace suppliers, engineering businesses, manufacturers, MRO organisations, and eligible defence supply-chain environments worldwide. Restricted programmes need a separate eligibility assessment before any access.
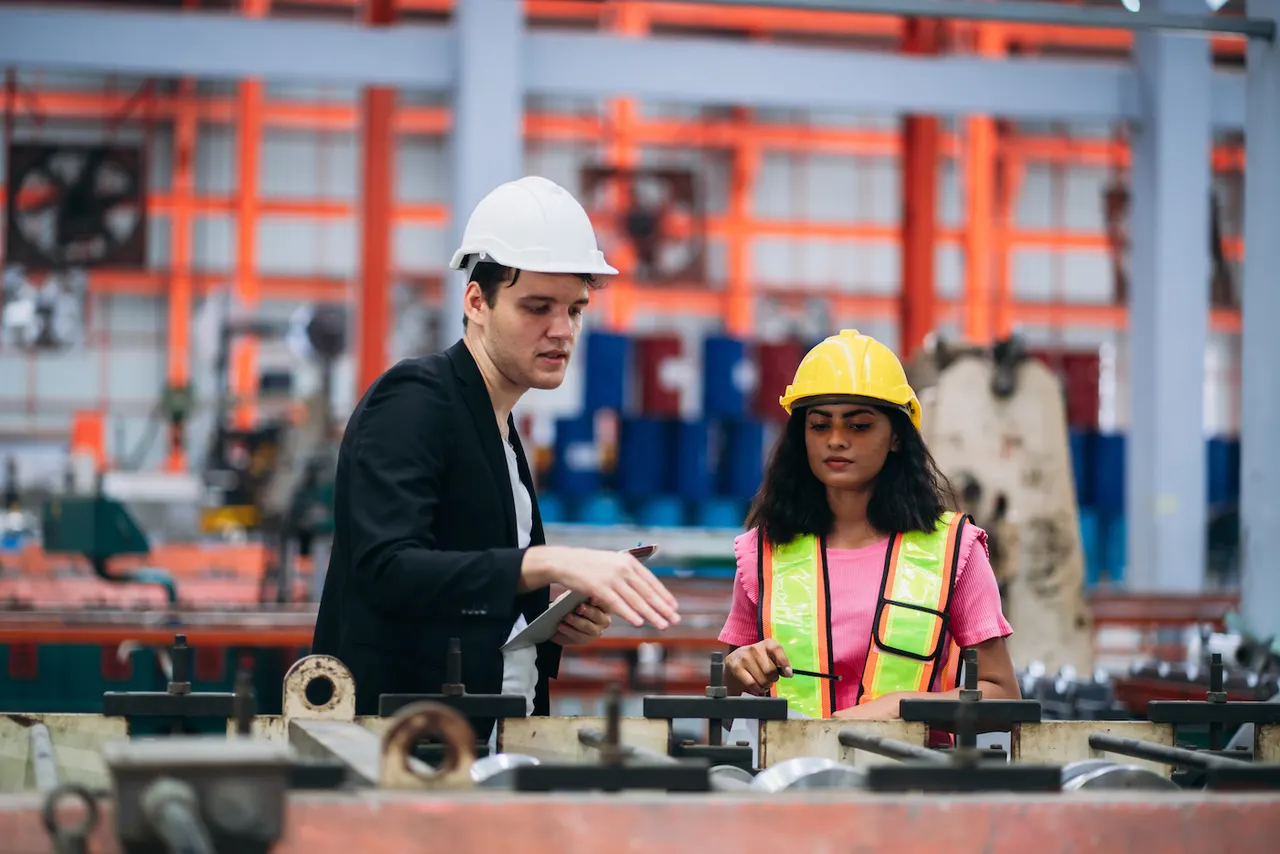
Protect engineering releases, supplier exchanges, production-support applications, test systems, and delivery evidence.
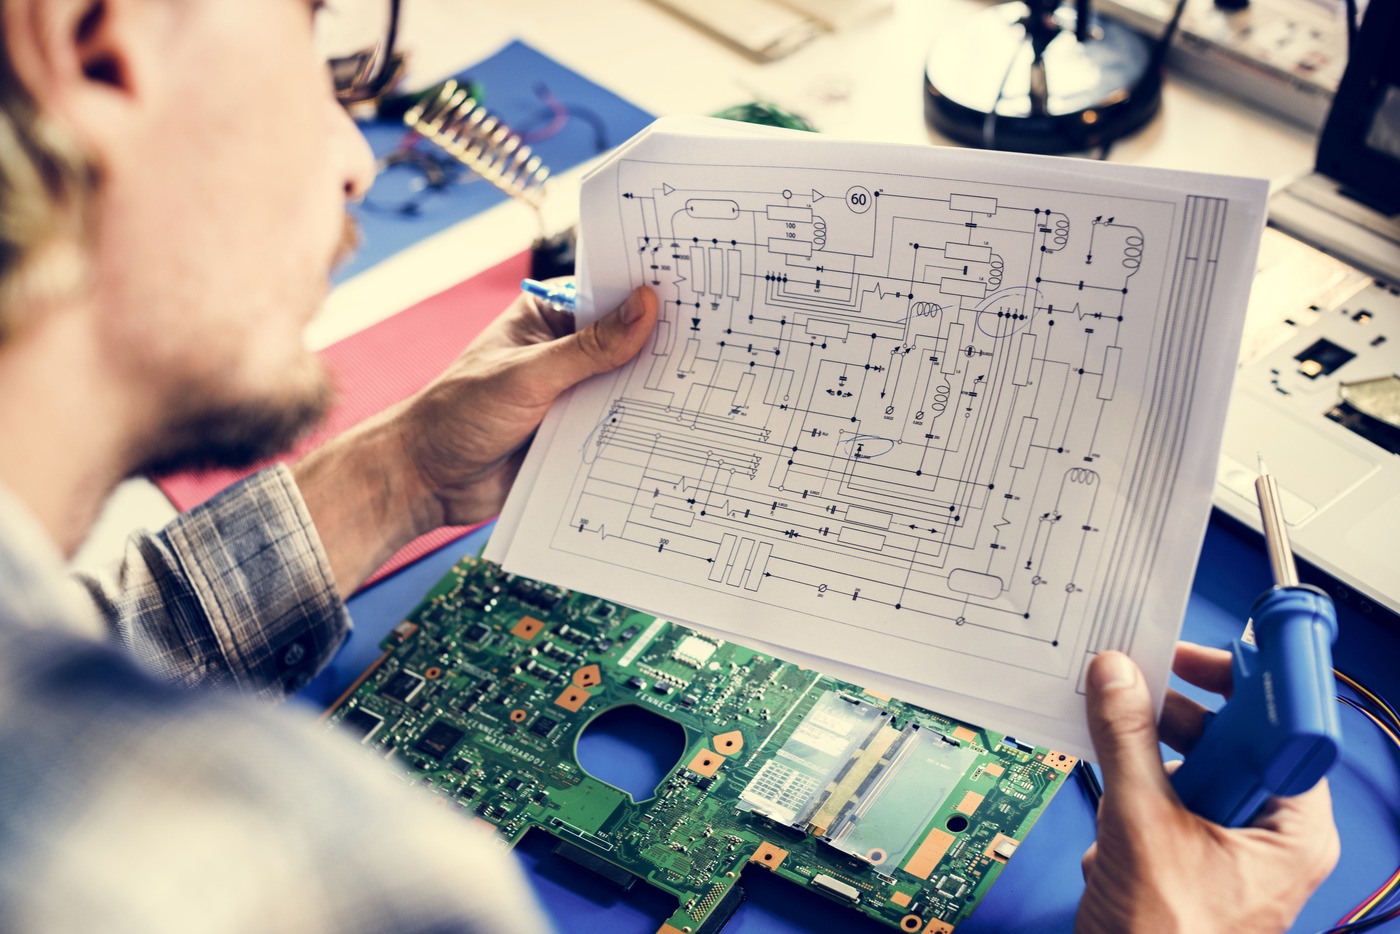
Strengthen programme separation, technical-data access, collaboration, source repositories, and customer-specific handling controls.
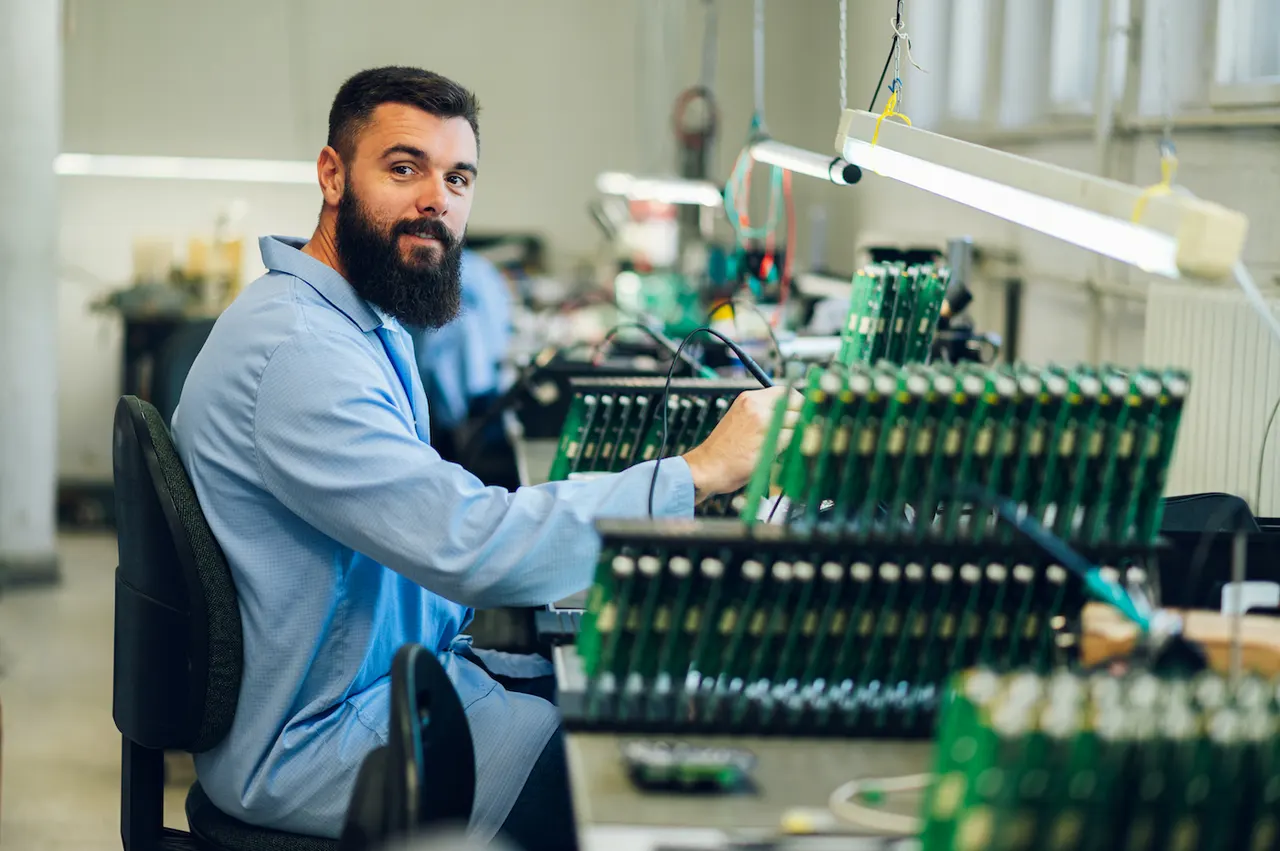
Review work-package systems, technical publications, maintenance records, parts traceability information, and support-tool access.
Assess eligible enterprise environments and organise evidence against applicable customer requirements, subject to classification, export, personnel, and contractual restrictions.
Work alongside your engineering and IT teams
We coordinate with your IT, engineering, quality and operations owners, using only the people, locations and access routes your authorised teams approve.
03Security risk and programme-boundary assessment
Establish what needs protection and who is authorised to act
An aerospace business can support several customers with different information-handling and assurance requirements.
We map the selected programme's systems and dependencies, identify responsibilities, and turn observed exposures into a practical improvement plan. Access eligibility is established before restricted material enters an assessment.
What we cover
- 01
Programme dependencies
Selected engineering, production, maintenance, business and identity services, mapped to the work they support.
- 02
Information categories
Customer-designated sensitivity, contractual handling instructions, approved environments and open classification questions.
- 03
System boundaries
Programme workspaces, shared services, supplier interfaces and paths into restricted environments.
- 04
Responsibility mapping
Who owns technical approval, access authorisation, system operation, security changes and external reporting.
- 05
Exposure review
Agreed external services, unsupported software, privileged access and dependencies with limited recovery options.
- 06
Remediation priorities
Findings ranked by exposure, affected workflow, constraints and the evidence needed to verify improvement.
04Engineering data, PLM, and technical-information protection
Make technical information accessible only through approved paths
Product lifecycle management (PLM), CAD, document repositories and file exchanges hold valuable programme knowledge. We review selected access and sharing controls around it, including copies outside the main engineering system.
- 01Data locationsAgreed drawings, models, specifications, test evidence and exported packages across repositories and storage.
- 02Programme permissionsRoles, inherited access, project separation and approval for sensitive downloads or bulk exports.
- 03Supplier exchangesApproved transfer channels, recipient restrictions, package access, expiry and handling instructions.
- 04Release integrityVersion identification, change attribution, release permissions and traceability to distributed copies.
- 05Retained copiesLocal downloads, collaboration links, backup handling, project closure and approved disposal.
- 06Access evidenceUseful logs, exception records, periodic reviews and escalation for unexpected sharing or changes.
05Workforce, supplier, and engineering-support access
Limit access to the person, programme, and period that require it
Programme engineers, subcontractors, machine vendors and software providers need different privileges. We help replace unclear or persistent access with attributable permissions, defined approval and verified removal.
06Software development, build, and release security
Strengthen the path from source change to approved software package
Engineering tools, production applications, test equipment and connected products need a controlled delivery process. We assess selected repositories, build services, dependencies and release mechanisms.
07Manufacturing, laboratory, and test-system security
Reduce unnecessary access to equipment supporting production and verification
08 · MRO applications, maintenance records, and supplier portals
Protect the records and interfaces supporting maintenance work
Maintenance, repair and overhaul teams depend on accurate work packages, accessible technical information, and attributable records.
We assess selected maintenance applications and interfaces to understand who can retrieve, change, approve, or export information across customers, facilities, and service partners.
What we cover
09Incident readiness and engineering-operation recovery
Prepare to restore trusted workflows after disruption
10Customer assurance and requirement readiness
Turn applicable requirements into traceable engineering work
Supplier questionnaires and contract requirements need evidence that matches the environment being described.
We help your team identify the agreed control baseline, document scope, track implementation gaps, and prepare clear technical material for customers or independent assessors, connecting each claim to observed controls.
What we cover
Across the aerospace lifecycle
Security priorities across the aerospace lifecycle
Place security checks alongside programme decisions. Each stage links to the service on this page that addresses it.
References reviewed October 2026Priorities for assessment, not legal advice. Export controls, classification, CMMC, UK defence requirements and EASA Part-IS apply differently by organisation, contract and jurisdiction, and are confirmed with your authorised advisers.
11Hire a dedicated aerospace cybersecurity engineer
Hire a Dedicated Cybersecurity Engineer
Give a defined programme-security workstream consistent ownership. The engineer coordinates an agreed backlog across IT, development, engineering, quality and operations, with skills, working hours, permitted location, personnel eligibility and specialist escalation confirmed before access begins.
01What the engineer can own
- Agreed risk, access-review and remediation backlogs
- Assessments of selected configurations, applications and builds
- Approved technical changes and retests
- Scoped exercises and customer-assurance records
02How they work with you
- Named accounts and customer-approved access routes
- Programme separation and handling instructions
- Engineering, quality, operations and security owners
- Export, safety and certification questions escalated
03How you see progress
- A prioritised plan with owners and acceptance checks
- Traceable findings and evidence of remediation
- Clear reports on exceptions and open exposure
- Priorities updated as programmes change
One engineer does not replace a cleared security organisation, airworthiness authority, specialist OT team or round-the-clock response function. Availability and appropriate support must be confirmed.
12Frequently asked questions
Frequently asked questions
Showing 19 of 19 questions
The proposed services address civil suppliers, manufacturers, engineering companies, MRO organisations, and eligible defence supply-chain environments. Confirm systems, programme restrictions, technical capability, and delivery arrangements during scoping.
This page focuses on engineering, manufacturing, supplier, and MRO workflows. Airline passenger systems, airport operations, and air traffic services need separately defined scope and expertise.
Yes. A defined engineering workspace, supplier-access review, maintenance application, build environment, or recovery exercise can establish a practical starting point, subject to appropriate authorisation.
Discuss the required technical profile, permitted access location, schedule, reporting line, and eligibility. Confirm availability and specialist escalation; general IT, OT, and airborne-product security are different skill sets.
Only after your authorised team confirms that the proposed people, locations, information, and activities are permitted. Contracts, export rules, classification, and customer conditions may restrict access. Offshore delivery must never be assumed from ordinary account permission.
Classified work is outside this proposed offering. Other restricted work requires a separate eligibility assessment and explicit authorisation before access. Do not send classified or controlled material through an enquiry form.
No. Controlled Unclassified Information (CUI), export controls, classification, and contractual restrictions are distinct concepts that may overlap. Your responsible authorities determine the applicable categories and handling rules.
Not by itself. Remote viewing, screen sharing, support evidence, administrative access, or technical assistance may still require review. Hosting location and encryption are controls, not blanket authorisation.
We can propose scoped gap analysis, remediation coordination, and evidence preparation where access is permitted and expertise is verified. Certification or assessment status must come through the applicable authorised process. No certification or contract award is guaranteed.
As checked on 25 October 2026, official guidance states that Phase II was suspended on 13 July 2026 and implementation remains in Phase 1. Applicable safeguarding, Phase 1 self-assessment, and affirmation requirements remain in force; the suspension does not remove existing contractual cybersecurity obligations. Do not assume the former 10 November 2026 Phase II date applies. Check current solicitation, contract, and deviation requirements with your contracting team.
Revision 3 is NIST's newer final publication; that does not automatically replace the edition required by your contract. Current CMMC guidance still identifies Revision 2 for Level 2. Record the applicable clauses, deviations, assessment basis, and customer direction before mapping controls.
Readiness work can be scoped against applicable customer requirements. UK government guidance describes Cyber Security Model version 4, contractual risk profiles, supplier questionnaires, and Defence Cyber Certification. Confirm the assigned profile and contractual process; Nestack does not issue DCC certification.
No. Applicability depends on the organisation and its approvals, with stated exceptions. Relevant design and production organisations and certain maintenance organisations fall within defined categories. The two regulations have different application dates: 16 October 2025 and 22 February 2026. Confirm your specific position with the responsible aviation authority and advisers.
Only under separately authorised scope with eligible personnel, appropriate expertise, and an approved representative environment. Live aircraft and safety-related systems are not included in ordinary enterprise application testing.
No. Security findings can inform the responsible engineering and assurance teams. Airworthiness, maintenance release, process qualification, and product acceptance remain separate decisions under the applicable approval framework.
Begin with documentation, configuration review, and suitable test environments. Live equipment work requires site coordination, explicit permissions, compatible methods, and stop conditions. No assessment should promise zero operational risk.
Not automatically. Agree coverage, response hours, specialist responders, evidence handling, and reporting responsibilities separately. A dedicated engineer engagement does not imply continuous monitoring.
Agreed outputs may include dependency maps, access matrices, technical findings, requirements mappings, remediation records, retests, and exercise reports. Evidence distinguishes observed results, assumptions, exclusions, and unfinished work.
Describe your organisation type, broad system categories, main concern, and preferred engagement. Do not attach technical drawings, controlled data, aircraft configurations, credentials, or incident evidence. An appropriate channel can be agreed after eligibility review.
Contact and scoping call
Discuss your aerospace and
defence security priorities.
Tell us where you need support: engineering information, supplier access, software delivery, manufacturing and test systems, MRO applications, recovery planning, customer assurance, or a dedicated engineer.
Loading open times…
Open times
Select an available date above to view open 45-minute times from our calendar.