
Automotive cybersecurity
Automotive Cybersecurity
Expertise for Your Team
Strengthen security across automotive engineering, operations, and connected services. Protect programme information, supplier access, production dependencies, and digital customer services, and build a practical improvement plan with clear boundaries between business systems, factory equipment, and vehicle products.
An automotive programme combines engineering files, supplier exchanges, production systems, software releases, and after-sales services.
A shared identity or integration can connect activities with very different operational consequences.
Nestack helps your IT, engineering, manufacturing, and digital teams assess selected exposures, implement approved controls, and verify changes. Each engagement defines the relevant systems, responsible owners, and specialist support before work starts.
Three ways to work with Nestack
- 01
Scoped assessment
Review a programme workspace, supplier connection, application, plant dependency, or software-delivery process.
- 02
Dedicated security engineer
Add capacity with an agreed profile, backlog, working hours, and reporting line.
- 03
Ongoing improvement
Coordinate approved remediation, access reviews, retests, recovery exercises, and customer-assurance evidence.
Engineering release, vehicle safety, production restart, and business risk acceptance remain with authorised customer teams.
02Who we help
Support aligned with automotive responsibilities
For automotive manufacturers, component suppliers, engineering teams, dealer groups, and automotive software businesses worldwide.
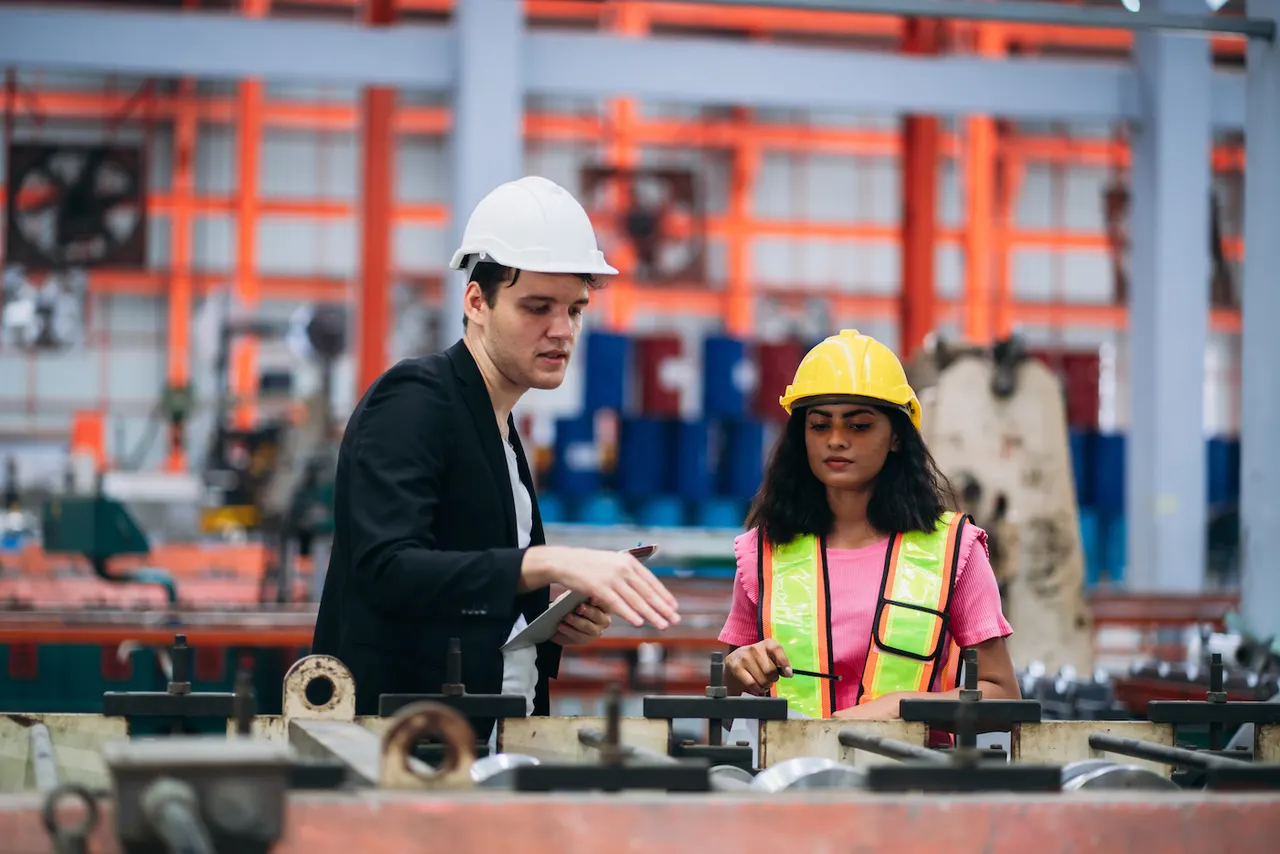
Protect engineering information, supplier collaboration, production-support systems, and programme-specific obligations.
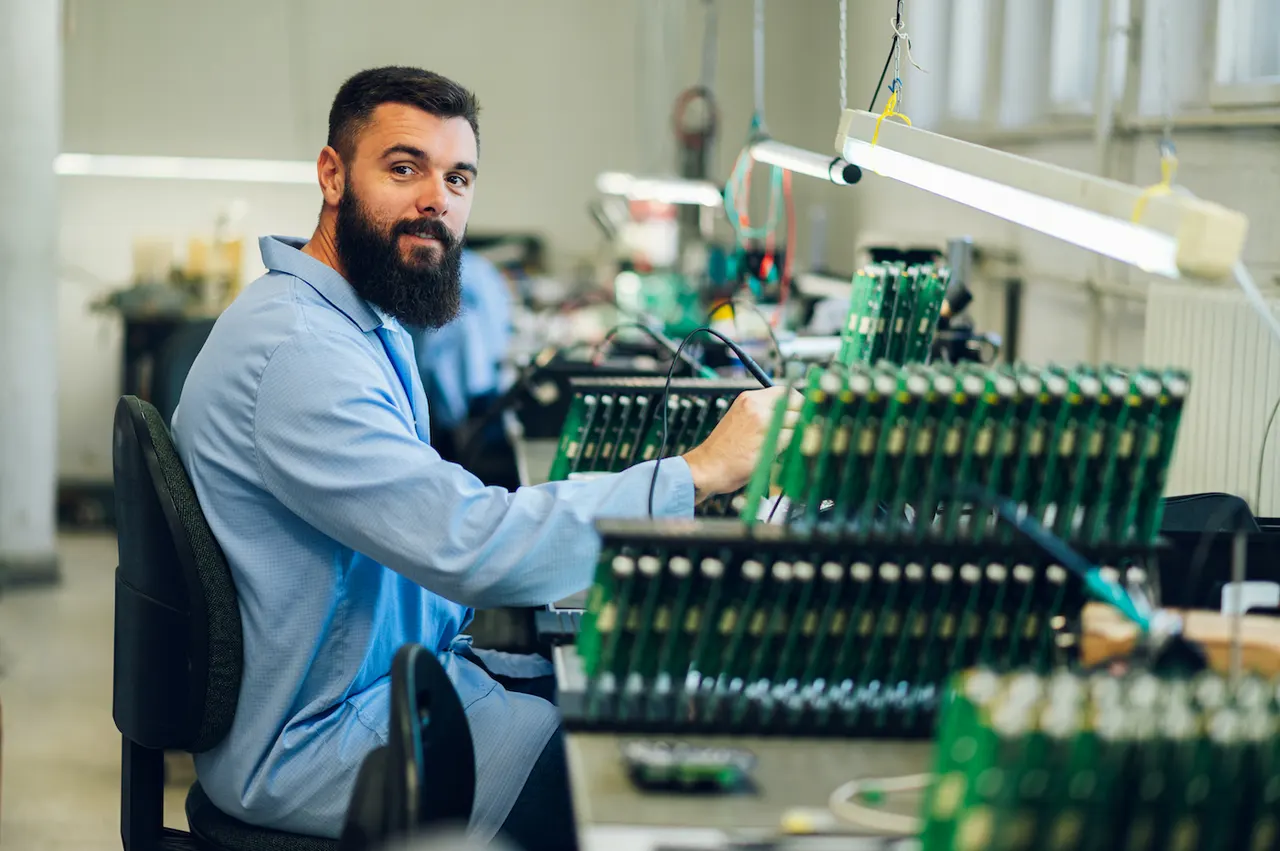
Strengthen source repositories, build infrastructure, technical interfaces, and security evidence delivered to customers.
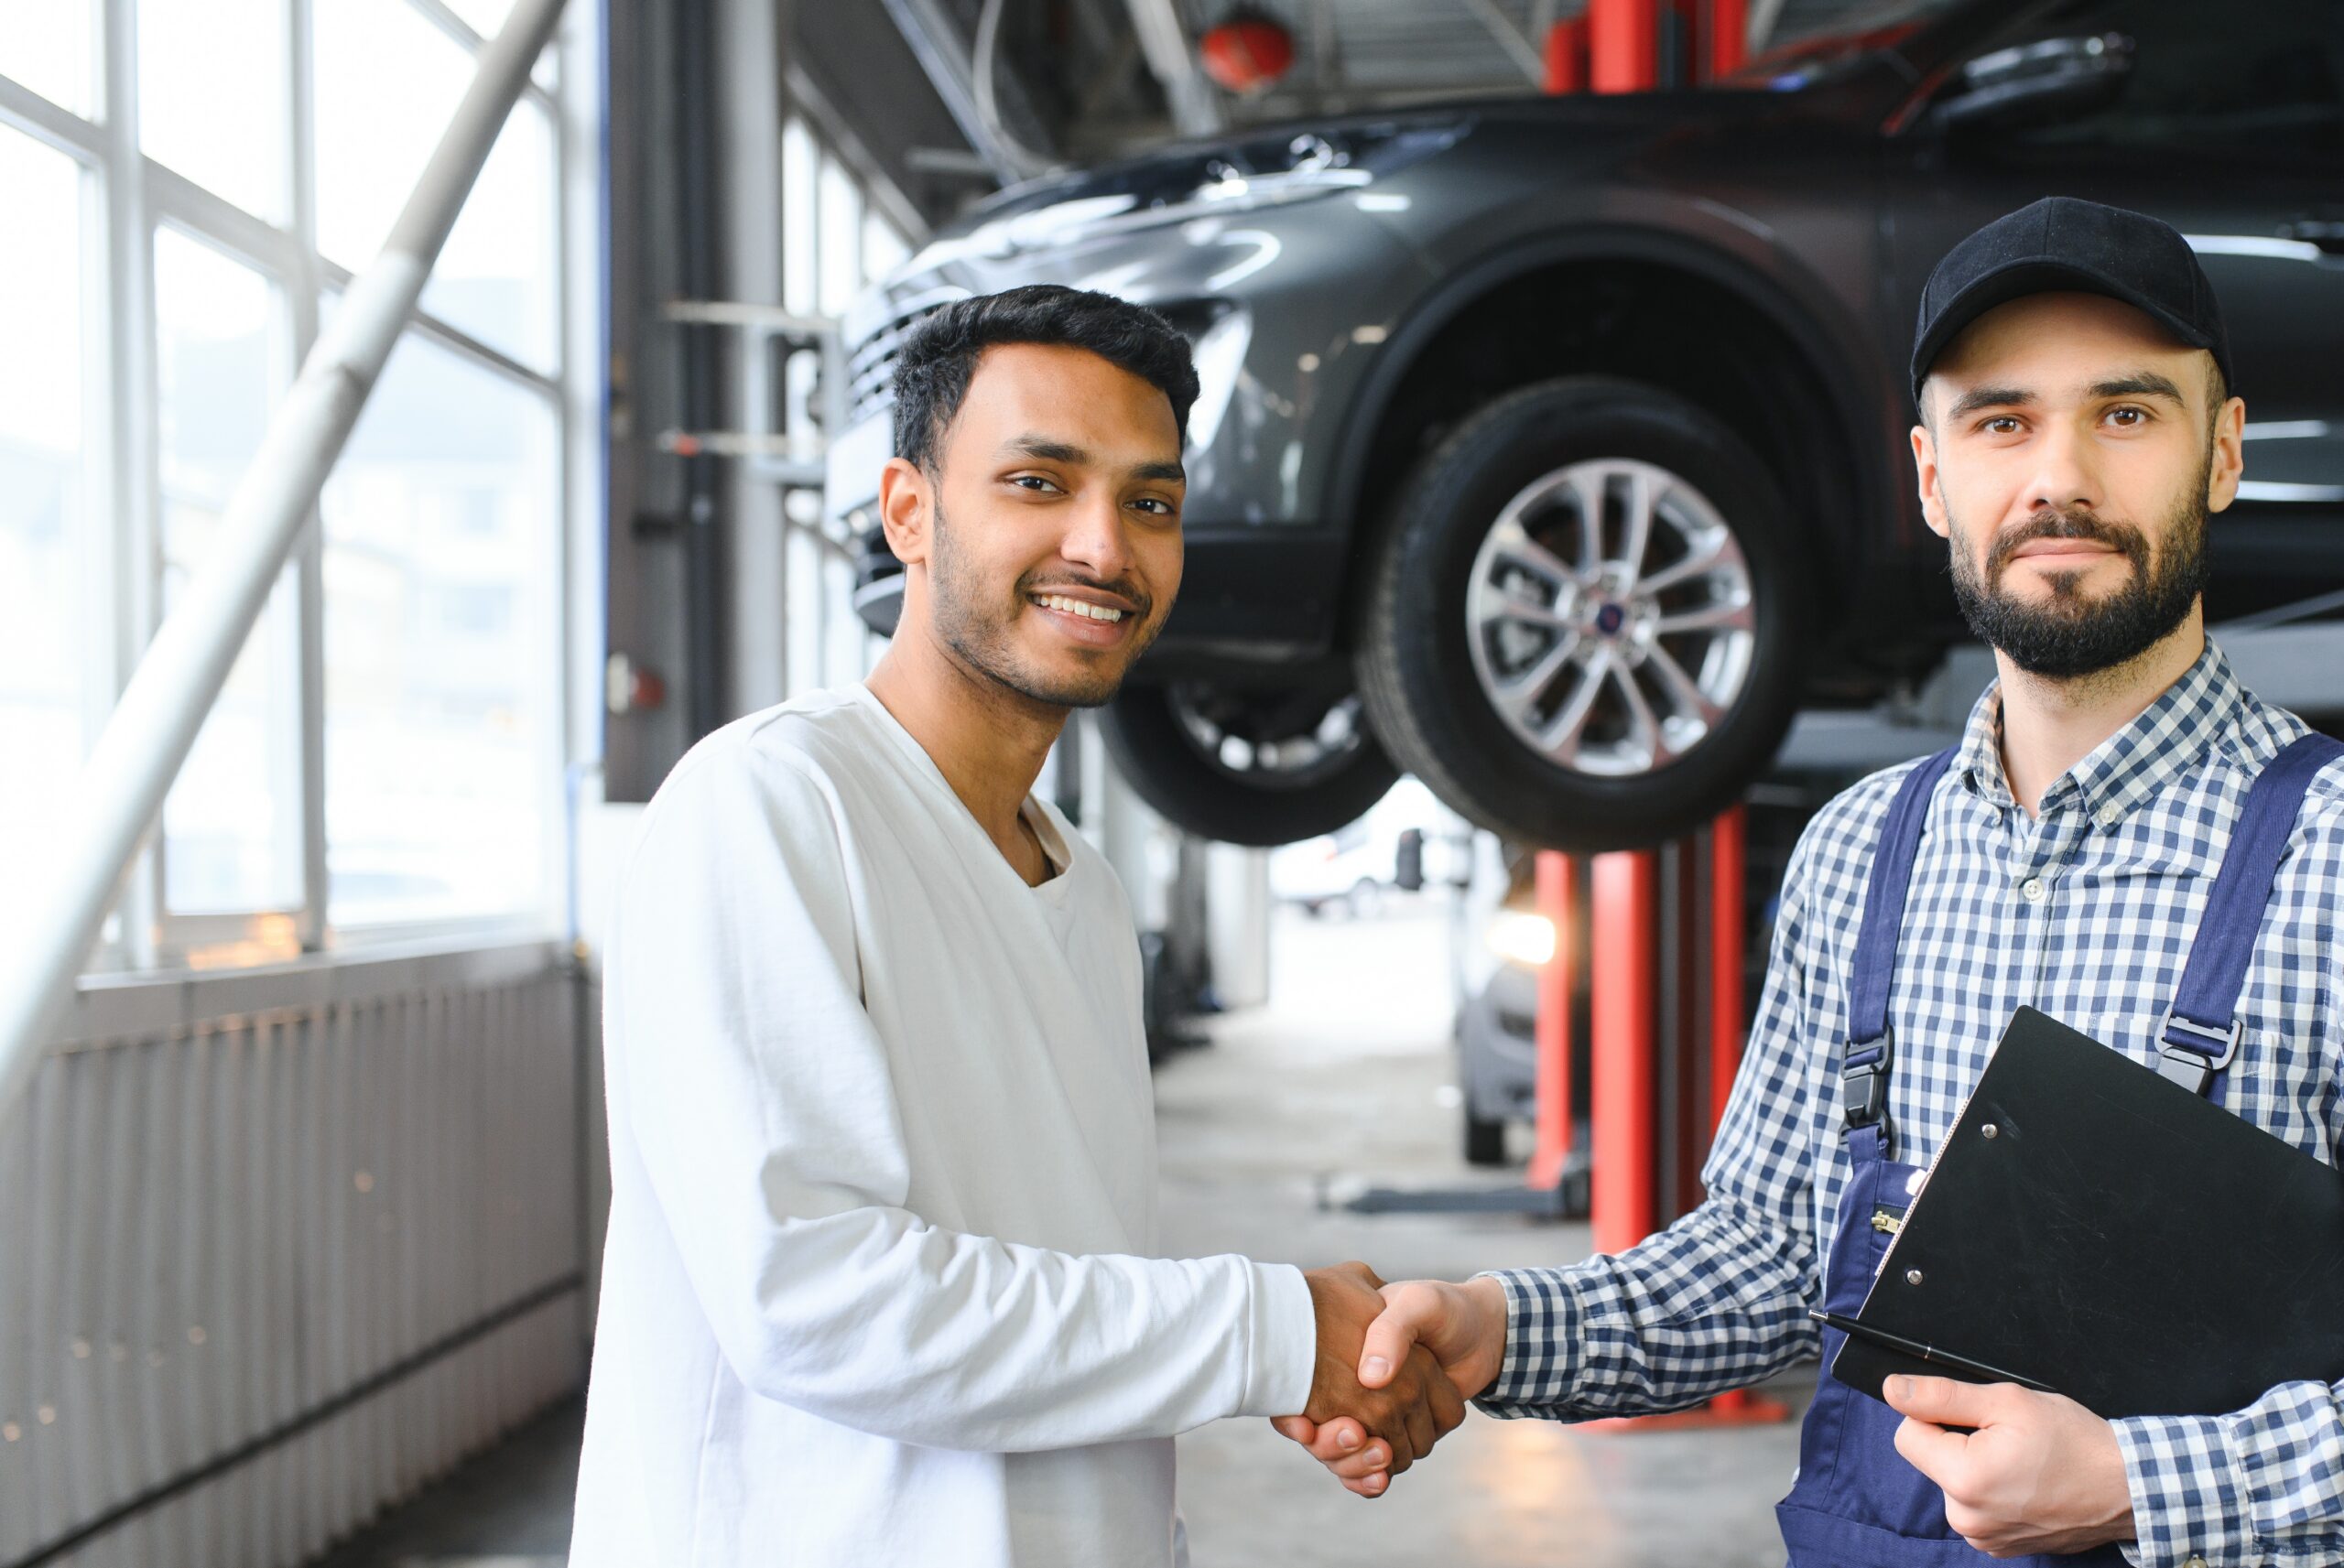
Review customer records, dealer-management applications, service tools, partner access, and recovery dependencies.
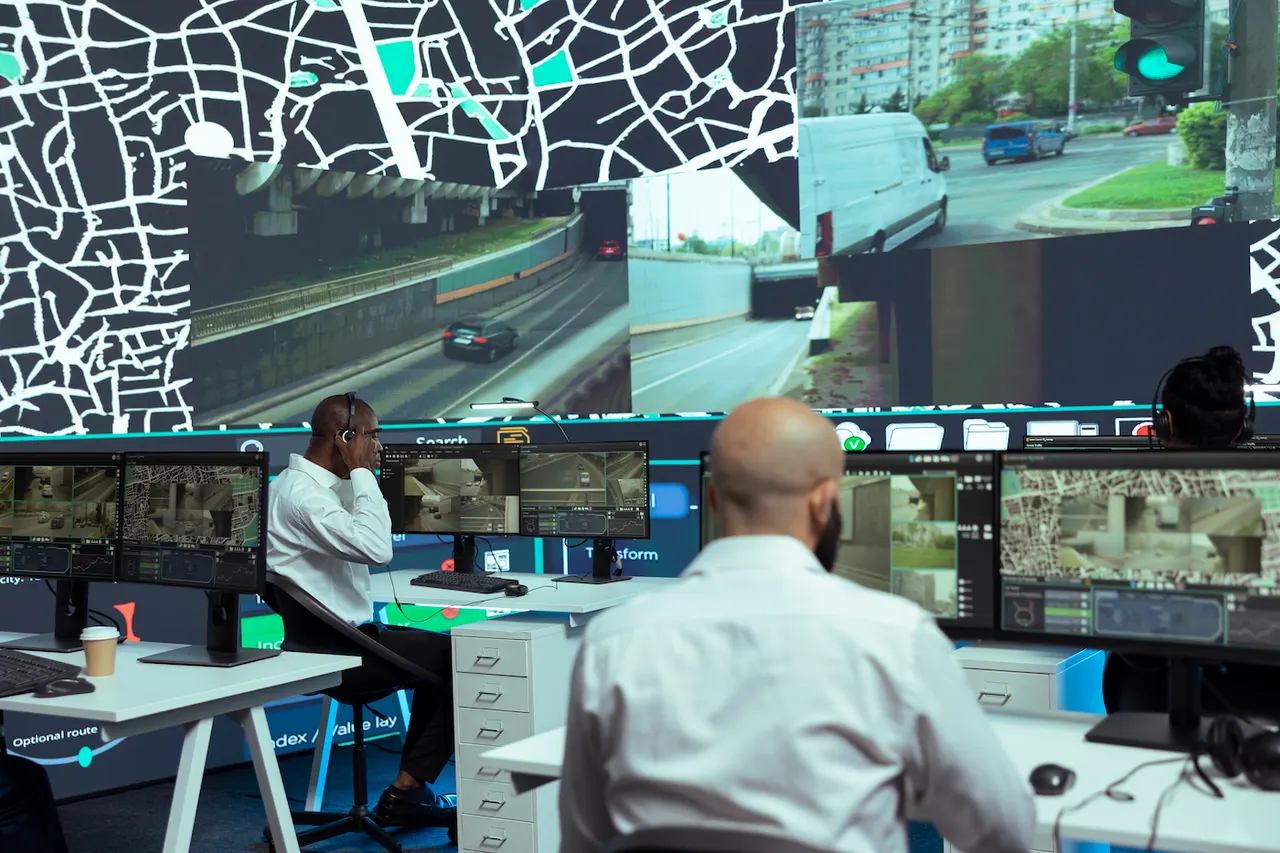
Assess customer, driver, and vehicle permissions across applications, cloud services, and authorised update infrastructure.
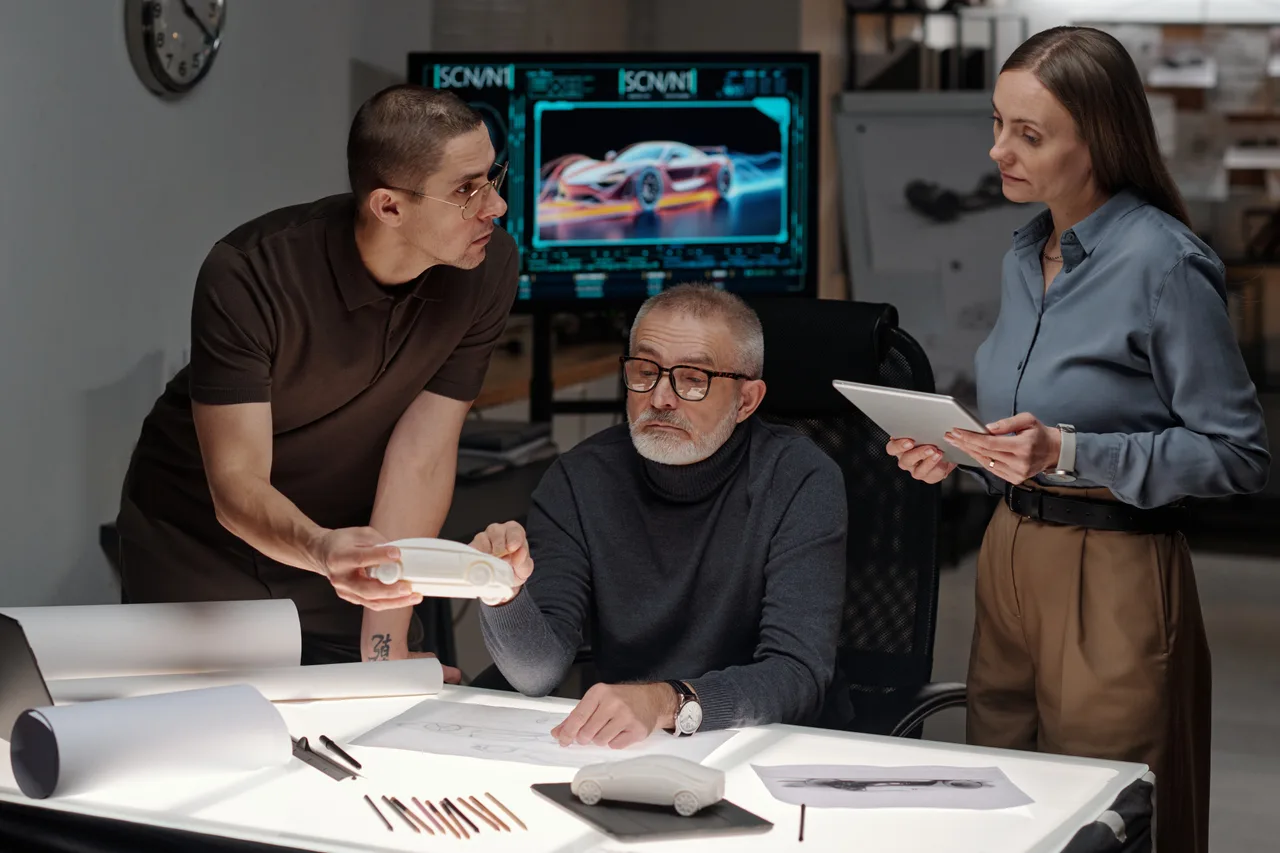
Work alongside your IT, engineering, plant and digital teams
We work with your IT, engineering, manufacturing and digital owners, within a scope agreed before work starts.
03Automotive risk, scope, and customer-assurance assessment
Establish the right security boundary before implementing controls
Automotive customers may request different evidence for information security, plant resilience, and vehicle cybersecurity.
We map the selected environment and requirements so the improvement plan reflects the systems and responsibilities actually in scope.
What we cover
- 01
Programme dependencies
Engineering, business, factory-support and connected-service systems, each with a responsible owner.
- 02
Scope separation
Enterprise information security, operational equipment and vehicle-product engineering kept distinct.
- 03
Customer requirements
Applicable contracts, assessment objectives, cited editions and evidence requests, recorded.
- 04
Shared services
Identity, hosting, supplier and support dependencies that cross programme boundaries.
- 05
Control evidence
Agreed requirements compared with configurations, procedures, exceptions and observed practice.
- 06
Remediation priorities
Actions, dependencies, acceptance checks and honest status reporting, each assigned.
04Engineering IP, prototype information, and supplier access
Control how programme information moves between organisations
Drawings, models, prototype images, software specifications and supplier quotations pass through several teams. We review selected product lifecycle management (PLM), collaboration and transfer systems around approved access and release decisions.
- 01Information locationsAgreed design files, test records, prototype material, exports and working copies.
- 02Programme separationRoles and inherited access across customers, vehicle programmes and supplier workspaces.
- 03Release integrityVersion identification, change attribution, approved packages and withdrawal of superseded material.
- 04Partner sharingRecipient restrictions, approved transfer channels, review links and permitted downloads.
- 05Identity lifecycleStrong authentication, administrators, contractor expiry and support access.
- 06Integration removalOwnership and revocation of supplier accounts, service credentials and retained connections.
05Automotive plant, test-bench, and workstation security
Reduce unnecessary access to production and verification systems
Production equipment and test benches may rely on specialised operating systems, tools and supported configurations. We review selected operational technology (OT) with site and equipment owners, planning improvements around reliability and safe working conditions.
06Dealer, after-sales, and automotive business applications
Protect customer information and service-workflow authority
Dealer-management and after-sales systems connect customer records, parts, appointments, finance relationships and workshop activity. We assess selected applications and integrations to clarify who can retrieve information or change sensitive business records.
07Connected-service, telematics, and automotive API security
Verify who may access each vehicle and perform each action
08Automotive software builds and update-delivery security
Protect the route from source change to approved update
Vehicle and component software may pass through multiple suppliers before release.
We review selected build and update infrastructure, concentrating on identities, artefact integrity, targeting and evidence of authorised publication.
What we cover
09 · Vehicle-product cybersecurity engineering support
Build evidence for a defined product-security workstream
For teams developing vehicle electronics or software-enabled components, security work needs a clear product boundary and agreed supplier responsibilities.
We can scope specialist support for selected threat analysis, requirements, design reviews and verification activities.
What we cover
10Automotive incident readiness and operational recovery
Prepare coordinated decisions across business, plant, and product teams
Across the automotive lifecycle
Security priorities across the automotive lifecycle
Align checks with programme and ownership changes. Each stage links to the service on this page that addresses it.
References reviewed October 2026Priorities for assessment, not legal advice. UN R155 and R156 applicability, TISAX assessment, ISO/SAE 21434 and ISO 24089 work products, and FTC Safeguards Rule duties depend on market, vehicle category, scope and activity, and are confirmed with the manufacturer, approval authority, authorised audit provider or your advisers.
11Hire a dedicated automotive cybersecurity engineer
Hire a Dedicated Cybersecurity Engineer
Give an agreed automotive-security backlog consistent ownership. Match the engineer to enterprise, application, plant or vehicle-product needs, and agree working hours, permitted access locations, required equipment and specialist escalation.
01What the engineer can own
- Agreed risks, requirements and remediation actions
- Reviews of selected configurations, access, applications or evidence
- Coordinated approved fixes and retests
- Scoped exercises and customer-assurance material
02How they work with your teams
- IT, engineering, plant, product and service owners
- Named accounts and approved customer environments
- Programme confidentiality and change procedures
- Safety, release, regulatory and financial decisions escalated
03How you see progress
- A prioritised backlog with owners and dependencies
- Evidence of verified fixes and completed work products
- Clear reporting on exceptions and residual exposure
- Priorities revised as programmes and suppliers change
One engineer does not replace an authorised assessor, vehicle-safety team, onsite equipment specialist or 24/7 response function. Availability and support arrangements are confirmed in the engagement.
12Frequently asked questions
Frequently asked questions
Showing 19 of 19 questions
The proposed services cover manufacturers, component suppliers, engineering teams, dealer groups, and connected-service businesses. Confirm systems, specialist capability, and delivery scope first.
No. Factory work concerns systems used to manufacture or test products. Vehicle cybersecurity concerns the delivered vehicle and its supporting services. Scope and expertise must be agreed separately.
Yes. A supplier-access review, engineering workspace, dealer application, backend API, or recovery exercise can establish a practical starting point.
Discuss responsibilities, technical profile, working hours, reporting, and specialist escalation. Confirm availability. Enterprise, OT, embedded, and vehicle-security roles are not interchangeable.
Agree personnel, permitted locations, confidentiality, customer-controlled access, and evidence handling. Some programme contracts or data restrictions may limit offshore access even when files remain locally hosted.
Scoped gap analysis, remediation, and evidence preparation can support readiness. Formal assessments use authorised audit providers and defined scope, locations, and objectives. Nestack does not grant TISAX labels or imply assessor status.
No. It addresses cybersecurity engineering for road-vehicle electrical and electronic systems. Applying it does not automatically provide regulatory approval, functional-safety conformity, or certification.
No. Requirements depend on adopting markets, vehicle categories, approval routes, and applicable dates. R155 concerns cybersecurity and management systems; R156 concerns software updates and update management. Confirm the programme's obligations with the manufacturer and approval authority.
This engagement does not grant approval. VCA guidance distinguishes manufacturer vehicle approval from supplier evidence supporting manufacturer requirements. Agree the customer's allocated obligations and required work products.
Only under a separately authorised specialist plan with appropriate facilities and safety oversight. Ordinary application tests use synthetic vehicles or disabled command paths, not live actuation.
An agreed review can cover build, signing, distribution, targeting, and verification evidence. Actual update activation and vehicle compatibility require manufacturer-approved engineering and safety processes.
Yes, where expertise and permission are confirmed. Begin with documentation and configuration review; live scanning or changes require site coordination, vendor constraints, and stop conditions.
An authorised assessment can examine roles, customer records, integrations, and sensitive actions. Testing a dealer system does not authorise access to finance providers or connected vehicles.
No. FTC guidance concerns relevant US financial institutions, including many dealers arranging financing or leasing. Applicability and covered information require review; ordinary service data is not automatically covered merely because a dealer holds it.
Yes, within an authorised connected-service scope. Review account-to-vehicle relationships, previous-user removal, credentials, and retained information using safe test cases.
No. Security findings can inform safety engineering, but functional safety, roadworthiness, production acceptance, and vehicle release require their own responsible processes.
Not automatically. Agree coverage, specialist responders, reporting responsibilities, and escalation separately. Product incidents may require manufacturer-led action beyond enterprise incident response.
Scope depends on systems, vehicle relevance, access, hardware, testing depth, programme requirements, and specialist needs. Agree milestones and acceptance evidence after discovery.
Describe your organisation, broad systems, concern, and preferred engagement. Do not submit prototype files, vehicle keys, firmware, customer records, credentials, or incident evidence through the public form.
Contact and scoping call
Discuss your automotive
security priorities.
Tell us where you need support: programme information, supplier access, plant systems, dealer applications, connected services, software updates, product engineering, recovery, or a dedicated engineer.
Loading open times…
Open times
Select an available date above to view open 45-minute times from our calendar.