
Biotechnology cybersecurity
Biotechnology Cybersecurity
Expertise for Your Team
Protect the information and systems behind your biotechnology programmes. Strengthen research confidentiality, laboratory access, data integrity, and recovery readiness, with security controls built around how your scientists, partners, and technology teams work.
A biotechnology programme may connect research notebooks, sample records, instrument workstations, analysis pipelines, external laboratories, and clinical-development systems.
Those connections can expose confidential work or interrupt an activity that cannot simply be repeated tomorrow.
Nestack helps your teams assess selected systems, implement approved safeguards, and verify improvements. We connect findings to the scientific, quality, privacy, and operational owners who decide how changes should be accepted.
Three ways to work with Nestack
- 01
Targeted assessment
Examine a laboratory application, collaboration workspace, analysis environment, or recovery dependency.
- 02
Dedicated security engineer
Add capacity with a defined technical profile, backlog, working hours, and reporting line.
- 03
Ongoing improvement
Coordinate access reviews, remediation, retests, supplier evidence, and controlled exercises.
Security support complements your scientific and quality systems; it does not replace their approval processes.
02Who we help
Support for different biotechnology operating models
For biotechnology innovators, research organisations, laboratory service providers, and authorised development partners worldwide.
Protect programme knowledge, experimental records, investor data rooms, and collaboration as teams grow.
Assess approved research workspaces, dataset access, analysis pipelines, and cloud permissions.
Strengthen sponsor separation, laboratory applications, instrument-support access, and delivery records.
Review selected technology-transfer, quality-system, trial-platform, and manufacturing-support dependencies with responsible specialists.
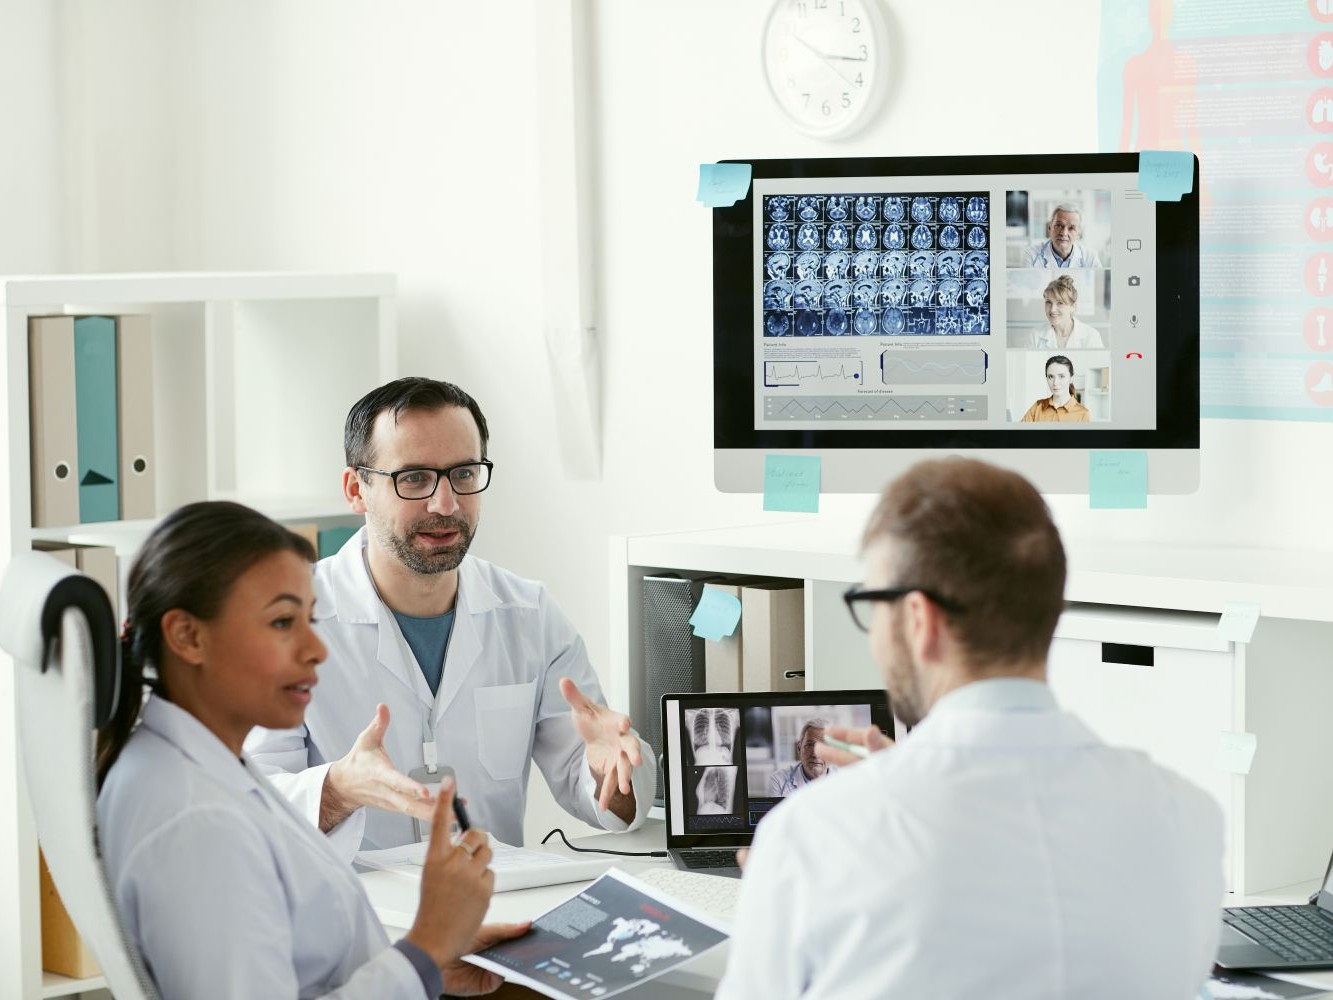
Work alongside your research, laboratory, quality and IT teams
We work with your research, laboratory, quality and technology owners, within a scope agreed before work starts.
03Biotechnology programme risk and dependency assessment
Start with the programme, its information, and its critical dependencies
Security priorities differ between exploratory research, a regulated study, and a manufacturing-support workflow.
We define the selected programme boundary before recommending changes, including who owns information and who can approve access.
What we cover
- 01
Programme mapping
Agreed research, laboratory, analytical, collaboration and development systems, identified.
- 02
Information classification
Confidential knowledge, participant information, controlled datasets and regulated records, distinguished.
- 03
Dependency ownership
Identity, hosting, instruments, partners, licences and support responsibilities, documented.
- 04
Requirement scoping
Relevant agreements, study conditions, quality processes and jurisdictional obligations, recorded.
- 05
Exposure review
Selected access, sharing, configuration, recovery and evidence-management gaps.
- 06
Remediation planning
Priorities, responsible owners, operational dependencies and acceptance checks.
04Electronic laboratory records and LIMS security
Protect record access, attribution, and supporting context
Electronic laboratory notebooks (ELNs) and laboratory information management systems (LIMS) connect samples, activities, results, and review decisions. We examine selected permissions and interfaces so information remains attributable and available to authorised users.
05Research IP and external collaboration security
Share programme information with the right partners
Research programmes often involve universities, contract research organisations (CROs), contract development and manufacturing organisations (CDMOs), and specialist advisers. We review the practical access behind those relationships, including what persists after a project ends.
- 01Workspace separationSponsor, programme, partner and confidential due-diligence boundaries.
- 02Recipient controlsInvitations, approved domains, shared links, downloads and external administrators.
- 03Identity protectionAuthentication, account recovery, privileged roles and unmanaged access routes.
- 04Transfer approvalAgreed handover channels, release packages, version identification and recipient checks.
- 05Partner lifecycleOnboarding, scope changes, expiry, offboarding and service-credential removal.
- 06Evidence handlingSupport tickets, screenshots, logs and incident material protected from unnecessary research disclosure.
06Human research and controlled-access data security
Match data access to approved people, uses, and environments
Human research datasets may carry privacy, consent, repository, and contractual restrictions that continue beyond downloading a file.
We help implement selected technical requirements within an explicitly approved research environment.
What we cover
07Connected laboratory and instrument-workstation security
Reduce unnecessary access without interrupting laboratory work
08 · Bioinformatics, cloud pipelines, and AI permissions
Control what research software can read, change, and publish
Analysis environments combine notebooks, workflow engines, packages, containers, repositories, and cloud resources.
We assess selected infrastructure and software permissions, including AI assistants connected to research information.
What we cover
09Clinical-development platform and sponsor access security
Protect study boundaries and accountable changes
Biotechnology sponsors and their partners use electronic data capture, document repositories, and study-management tools. We review selected technical controls while preserving the responsibilities of sponsors, investigators, quality teams, and clinical providers.
10Biotechnology incident readiness and research recovery
Prepare to restore usable information and essential dependencies
Across the biotechnology lifecycle
Security priorities across the biotechnology lifecycle
Revisit safeguards as programmes and partners change. Each stage links to the service on this page that addresses it.
References reviewed October 2026Priorities for assessment, not legal or regulatory advice. FDA, HHS, NIH and WHO references apply by activity, record type, jurisdiction and agreement; your quality, privacy, legal and biosafety teams confirm the applicable requirements. Nestack does not certify compliance, grant data access or replace biosafety and biosecurity governance.
11Hire a dedicated biotechnology cybersecurity engineer
Hire a Dedicated Cybersecurity Engineer
Give an agreed research-security backlog consistent ownership. Match the role to your applications, cloud infrastructure, laboratory dependencies, and delivery constraints, and agree hours, specialist support, permitted locations, and reporting before access begins.
01What the engineer can own
- Selected risks, dependencies and remediation actions
- Reviews of approved access, software and configurations
- Coordinated technical changes and verified fixes
- Evidence, checklists and exercise material
02How they work with your teams
- Research, IT, laboratory and quality collaboration
- Approved accounts and controlled environments
- Confidentiality and change-control requirements
- Scientific, clinical, legal and safety decisions escalated
03How you see progress
- A prioritised backlog with accountable owners
- Evidence of retested controls and completed actions
- Clear records of exceptions and unresolved dependencies
- Regular reviews as programmes and partners evolve
Availability and scope are confirmed in the engagement. One engineer does not replace a validation team, privacy officer, biosafety lead, laboratory specialist, or 24/7 response function.
12Frequently asked questions
Frequently asked questions
Showing 19 of 19 questions
The proposed services cover research-stage companies, data-driven biotechnology, laboratory service providers, and development partners. Systems, specialist expertise, and permitted access determine the engagement.
Yes. A programme workspace, ELN, cloud-analysis environment, partner-access review, or recovery exercise can establish an achievable starting point.
Discuss the required profile, responsibilities, hours, reporting, and specialist support. Availability and permitted access are confirmed before commitment.
No. Repository terms, privacy law, agreements, approved-user conditions, and contractual restrictions must be checked. Keeping files in-country does not automatically authorise overseas administrative access.
Begin with synthetic records, configurations, and appropriately prepared evidence. Access to actual sensitive data requires explicit need, authority, environment approval, and handling controls.
An agreed assessment can examine roles, project separation, interfaces, change attribution, and recovery. Your laboratory and quality teams approve changes and determine required validation.
No. Applicable good-practice requirements depend on the activity and jurisdiction. Security evidence contributes to a broader quality and validation process; it does not establish full compliance or regulatory approval.
No. Applicability depends on the records, underlying FDA requirements, and use of electronic records or signatures. Responsible regulatory and quality teams should establish the relevant boundary.
Not automatically. Required context, source data, metadata, history, and usable formats must be considered. Quality owners determine the appropriate record and archive requirements for the workflow.
No. HIPAA scope depends on covered-entity or business-associate status and the relevant information and activity. Other privacy, consent, contractual, or research obligations may apply independently.
Technical gap analysis can support an approved institution's obligations under its access agreement. Current NIH requirements distinguish repository scope, agreement timing, user responsibilities, and third-party systems. Nestack does not grant access or make institutional attestations on your behalf.
Do not assume so. Identifiability, permitted use, consent, and disclosure restrictions require appropriate assessment. Security review does not authorise re-identification or new research uses.
Yes, within an authorised scope. Review programme separation, transfers, support identities, subcontractor boundaries, and closure. Contracts and quality responsibilities remain with the responsible parties.
Begin with documentation and approved configuration review. Any live tests need laboratory and vendor coordination, appropriate expertise, stop conditions, and a safe maintenance window.
An agreed review can examine data retrieval, connector permissions, downstream authority, and approval controls using fictional content. It does not validate scientific outputs or biological designs.
No. It supports protection of information and connected systems. Institutional oversight, physical controls, biological-risk assessment, and qualified laboratory practice remain essential and separately owned.
No coverage is assumed. Agree service hours, response capacity, specialist contacts, and escalation before relying on operational support.
Systems, data restrictions, testing depth, laboratory access, validation dependencies, and specialist needs shape the proposal. Agree milestones and acceptance evidence after discovery.
Describe your organisation, broad systems, concern, and preferred engagement. Exclude participant records, sequence data, confidential protocols, credentials, and incident evidence from the public form.
Contact and scoping call
Discuss your biotechnology
security priorities.
Tell us where you need support: programme information, laboratory records, collaboration, controlled data, connected instruments, research software, clinical platforms, recovery, or a dedicated engineer.
Loading open times…
Open times
Select an available date above to view open 45-minute times from our calendar.