
Energy & utilities cybersecurity
Energy & Utilities Cybersecurity
Expertise for Your Team
Protect the digital dependencies behind essential services. Strengthen access, information flows, and recovery readiness across utility business systems and selected operational environments, with improvements built around your service obligations, engineering constraints, and authorised change processes.
Utilities depend on control centres, remote sites, communications, field contractors, equipment vendors, customer systems, and external service providers.
A business-system identity or unnoticed support connection can create dependencies beyond its original purpose.
Nestack helps your IT, operations, engineering, and security teams assess agreed exposures, implement approved controls, and verify improvements. Begin with the systems and interfaces that matter to your organisation, while making site authority and testing restrictions explicit.
Three ways to work with Nestack
- 01
Focused assessment
Review a supplier route, operational boundary, customer application, distributed-energy integration, or recovery scenario.
- 02
Dedicated security engineer
Add agreed technical capacity with defined duties, access, reporting, and specialist escalation.
- 03
Ongoing improvement
Coordinate access reviews, remediation, evidence, supplier actions, and controlled exercises.
Operators retain dispatch, switching, treatment, safety, emergency, and restoration decisions.
02Who we help
Scope shaped around your operating responsibilities
For energy producers, network operators, renewable-energy businesses, distributed-energy providers, and water and wastewater utilities worldwide.
Review generation-support, control-centre, substation, business-system, and supplier dependencies.
Assess solar, wind, storage, aggregation, charging, and cloud-connected service interfaces within an agreed boundary.
Strengthen selected remote-site access, operational-support information, contractor workflows, and business applications.
Review treatment-support connections, telemetry, remote maintenance, customer systems, and incident preparation with qualified operational owners.
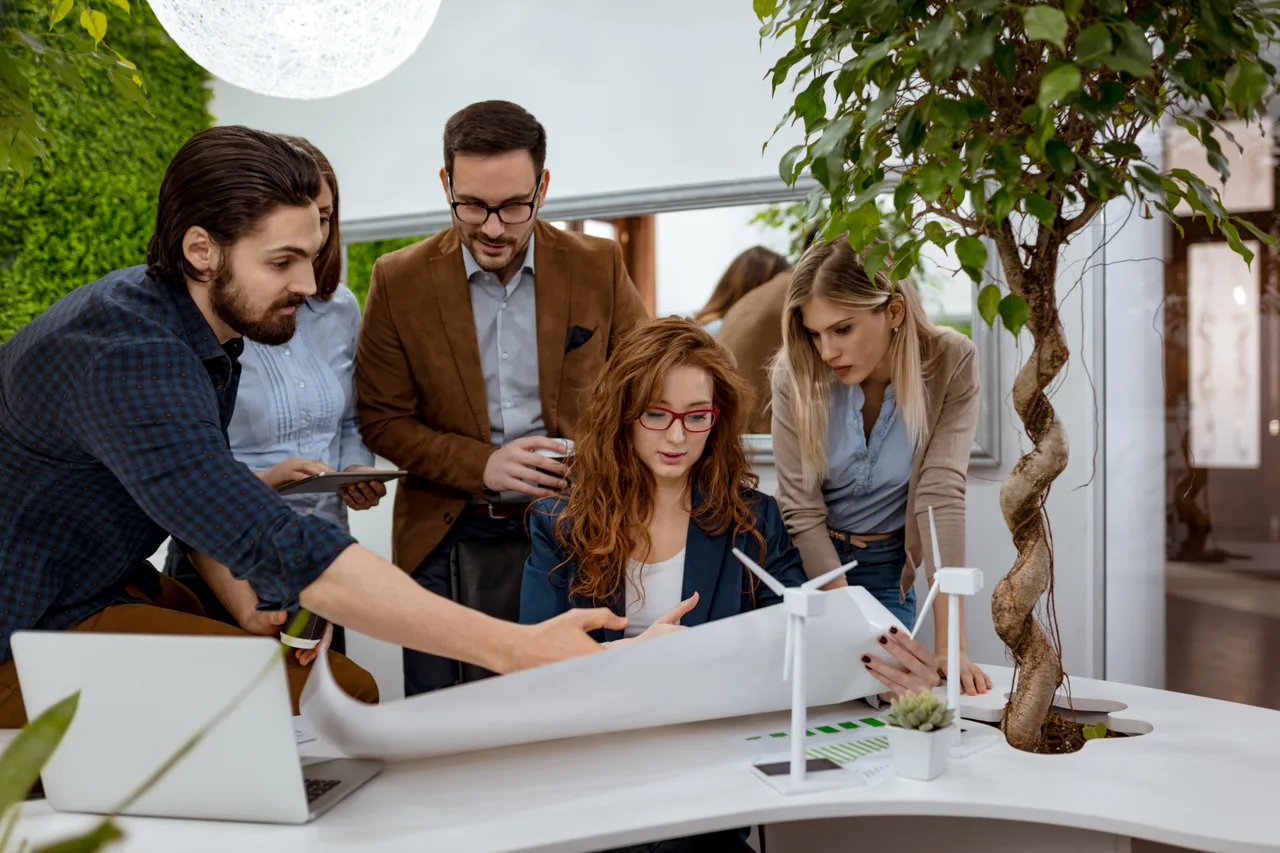
Work alongside your IT, operations and engineering teams
Electricity, gas, water, wastewater and distributed energy differ in obligations and engineering methods, so each scope is agreed with its operational owners.
03Utility risk and dependency assessment
Prioritise the digital dependencies behind your service obligations
A utility assessment needs a defined service, site, and system boundary.
We work with your owners to understand selected dependencies and identify where responsibilities, access, and evidence need improvement before proposing technical changes.
What we cover
- 01
Service context
The electricity, energy, water or wastewater activities covered by the engagement, identified.
- 02
Critical dependencies
Agreed identity, communications, hosting, power, time, vendor and licensing dependencies, mapped.
- 03
System ownership
Corporate IT, operational technology, field equipment, customer services and third-party platforms, distinguished.
- 04
Risk inputs
Technical findings connected with operator-defined service consequences and engineering constraints.
- 05
Obligation scope
Applicable jurisdictions, contracts, asset categories and requirements confirmed by responsible advisers.
- 06
Improvement planning
Priorities, accountable owners, prerequisites, maintenance windows and acceptance evidence.
04IT and operational-network boundary security
Reduce unnecessary paths into operational environments
05Vendor remote access and privileged identity
Make support access accountable across sites and suppliers
Equipment vendors, integrators, field contractors, and IT providers may maintain separate access routes. We review who can reach selected environments, why that access exists, and how permissions are approved, recorded, reviewed, and removed.
06Distributed-energy and connected services
Clarify authority across assets, aggregators, and cloud platforms
Distributed resources can connect site equipment, fleet management, aggregators, installers, and customer services. We assess selected digital relationships so permissions and evidence reflect the difference between viewing information and influencing physical operation.
07Operational information and telemetry integrity
Protect the context and permissions behind operational records
Telemetry, asset records, diagrams, meter data, and maintenance information move through many systems before teams use them.
We examine selected digital controls that preserve attribution, authorised change, and appropriate access across those information flows.
What we cover
08 · Customer, field-service, and business application security
Strengthen access to accounts, work orders, and utility interfaces
Customer portals, mobile workforce applications, billing interfaces, and supplier systems can expose sensitive records or privileged workflows.
We review selected applications with test accounts and representative synthetic data, paying attention to the operational actions connected to business processes.
What we cover
09Supplier assurance and cybersecurity evidence readiness
Turn requirements into owned evidence and practical supplier actions
Utilities often need evidence from equipment suppliers, platform providers, integrators, and internal teams. We organise selected requirements and supporting records so gaps are explicit and technical work can be assigned without overstating compliance.
- 01Requirement mappingOwner-confirmed laws, standards, contracts and internal policies, connected to the scoped assets.
- 02Supplier reviewRemote support, vulnerability notification, update availability, subcontractors and incident coordination.
- 03Procurement inputsSecurity questions for new equipment, hosted platforms, integration services and support renewals.
- 04Evidence organisationAccess reviews, configuration records, exercises, approvals and remediation, linked to named owners.
- 05Exception handlingUnsupported equipment, risk acceptance, compensating controls and review dates, documented.
- 06Assurance preparationMissing evidence, specialist assessments, independence needs and decision-maker sign-off.
10Incident and recovery exercises
Rehearse technical recovery alongside operator-led service restoration
Across the utility lifecycle
Security priorities across the utility lifecycle
Improve the controls around operational handovers. Each stage links to the service on this page that addresses it.
References reviewed October 2026Priorities for assessment, not legal, regulatory or engineering advice. NERC CIP, NIS2, the NARUC and DOE distribution and DER baselines, EPA water resources and national requirements apply by entity, function, asset, jurisdiction and edition, and several are voluntary or interim. Your responsible advisers confirm the applicable obligations. Nestack does not certify compliance, provide accredited audit or regulator approval, or operate grid, gas, water or nuclear systems.
11Hire a dedicated utility cybersecurity engineer
Hire a Dedicated Cybersecurity Engineer
Add technical capacity with clear operational boundaries. Agree a profile around your utility systems and priorities: a dedicated engineer can maintain the improvement backlog and support authorised technical work while operational decisions remain with your responsible teams.
01Access and technical improvement
- Review agreed identities, supplier routes and system configurations
- Support authorised application and integration remediation
- Maintain retest evidence and unresolved technical dependencies
02Coordination and readiness
- Track supplier actions and requirement evidence
- Coordinate approved access reviews and recovery exercises
- Prepare clear findings for engineering and business owners
03Responsibilities and delivery
- Agree scope, locations, hours, reporting and access conditions
- Confirm sector experience and specialist escalation arrangements
- Define acceptance criteria, stop conditions and handover duties
Onsite operations, control-room coverage, specialised OT work, and emergency response require separate agreement. A dedicated engineer is not a utility operator or incident commander.
12Frequently asked questions
Frequently asked questions
Showing 19 of 19 questions
The proposed services cover selected electricity, renewables, distributed energy, gas, water, and wastewater environments. Scope and expertise must match the activity; a single assessment does not cover every utility discipline.
Yes. A vendor-access route, operational boundary, customer portal, distributed-energy integration, or recovery scenario can provide a defined starting point.
Discuss the profile, responsibilities, access, hours, reporting, and specialist support. Relevant experience and availability must be confirmed before commitment.
Approved documentation, code, configurations, and test environments may be suitable. Infrastructure restrictions, personnel requirements, contracts, evidence handling, and access locations must be agreed. Essential onsite work requires separate arrangements.
Not by default. Begin with approved documentation and passive evidence. Active testing requires explicit site and vendor approval, suitable windows, stop conditions, and a recovery plan.
No such change is included in an ordinary assessment. Switching, dispatch, protection, interlocks, treatment, pressure, and safety-relevant settings require separately authorised engineering and operational processes.
No. Operational technology has different performance, reliability, safety, and vendor constraints. Its systems and interfaces must be explicitly scoped with the responsible owners.
No. Applicability depends on relevant jurisdiction, registered function, facilities, cyber-system categorisation, and individual standards. The published list includes enforced and future versions; confirm the applicable edition and effective date.
No. They are resources and recommendations for relevant distribution and DER environments. Regulatory adoption and contractual requirements may differ, and the current public implementation page still identifies its guidance as interim.
No. Energy, drinking water, and wastewater are included sectors, but entity scope, size criteria, exceptions, and national implementation matter. Responsible advisers determine current obligations and reporting requirements.
No. EPA's technical guidance is voluntary, while US community water systems serving more than 3,300 people have specific risk-assessment duties under SDWA Section 1433 that include cybersecurity. Wastewater and local requirements differ; confirm applicable obligations.
An agreed engagement can organise requirements supplied or confirmed by your responsible advisers and map technical evidence. Verify current notifications, commencement dates, covered entities, and assessor qualifications before making compliance commitments.
Selected identities, APIs, access boundaries, and handover workflows can be assessed. Physical commands and equipment settings use simulation or separately approved test arrangements; engineering teams retain grid and equipment decisions.
Yes, within scope, using test identities and synthetic records. Routine checks do not execute customer payments, disconnections, reconnections, or live work-order changes.
No. Controls can protect access, attribution, and transfer integrity. Calibration, measurement validity, treatment effectiveness, settlement correctness, and operational interpretation require qualified domain specialists.
No. Technical recovery produces evidence for the responsible owners. Energisation, plant restart, treatment, switching, and service reconnection depend on operational, engineering, safety, and regulatory acceptance.
No 24/7 coverage is assumed. Agree monitoring scope, response hours, escalation, specialist availability, and contractual responsibilities before relying on an operational service.
Sites, system scope, data restrictions, evidence quality, vendor constraints, testing depth, and approval dependencies shape the proposal. Confirm deliverables and acceptance criteria after discovery.
Describe your utility activity, broad systems, concern, and preferred engagement. Exclude sensitive site details, network diagrams, control configurations, credentials, customer data, and incident evidence from the public form.
Contact and scoping call
Discuss your energy and utility
security priorities.
Tell us where your team needs support: dependencies, operational boundaries, supplier access, distributed energy, information flows, applications, evidence readiness, recovery, or a dedicated engineer.
Loading open times…
Open times
Select an available date above to view open 45-minute times from our calendar.