
Home services cybersecurity
Home Services Cybersecurity
Expertise for Your Team
Protect customer information from the first booking to the final invoice. Strengthen security across office accounts, scheduling tools, technician devices, job records, and customer communications, with practical controls built around how your team serves households and coordinates field work.
A home-service job can involve an online enquiry, a dispatcher, subcontractors, photos, property notes, access instructions, and a payment link.
Those records may reveal more about a household than a simple customer contact list.
Nestack helps your team review selected exposures, implement approved improvements, and verify that access matches the work people need to perform. Start with your scheduling platform, office accounts, mobile devices, customer portal, or payment workflow and build a manageable improvement plan.
Three ways to work with Nestack
- 01
Focused assessment
Review one platform, customer-data workflow, device group, contractor process, or recovery scenario.
- 02
Dedicated security engineer
Add agreed technical support with clear duties, hours, reporting, and escalation.
- 03
Ongoing improvement
Coordinate access reviews, remediation, staff guidance, supplier actions, and recovery checks.
Your business retains service decisions, customer commitments, trade responsibilities, and permission to enter or work in a home.
02Who we help
Support shaped around your teams and service model
For repair, maintenance, installation, cleaning, pest-control, franchise, and home-service platform businesses worldwide.
Review HVAC, plumbing, electrical, appliance, and maintenance scheduling, technician access, job records, and invoicing systems.
Protect repeat-visit schedules, property notes, access instructions, contractor permissions, and customer communications.
Assess branch separation, central administration, shared platforms, outsourced support, and staff changes.
Review customer, provider, dispatcher, partner, and administrator boundaries across booking and service applications.
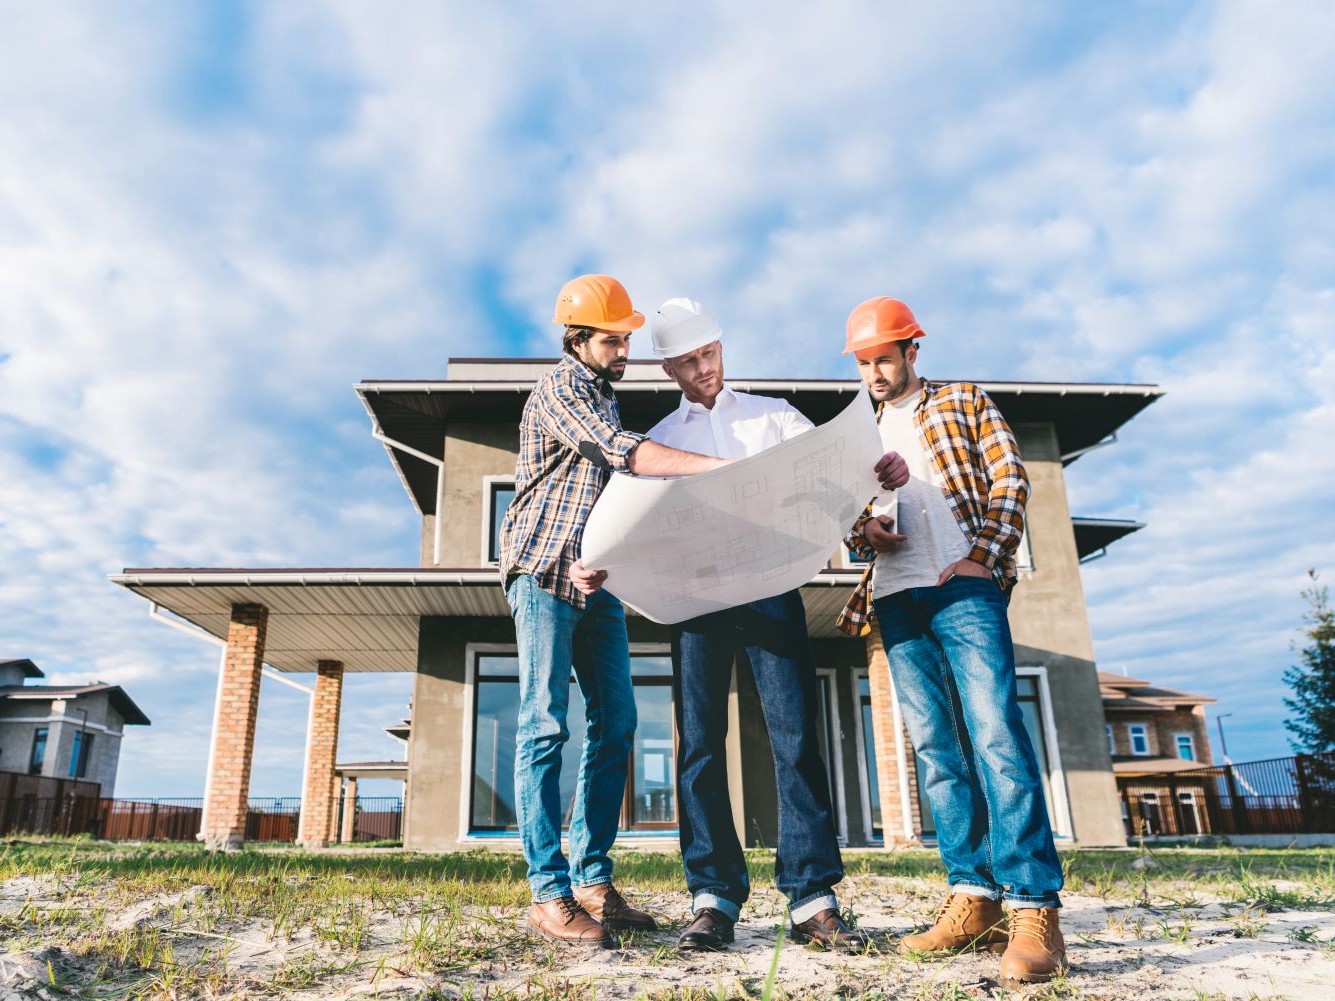
Work alongside your office, field and trade teams
We coordinate authorised improvements while your business keeps its service decisions, customer commitments and permission to work in a home.
03Home-service cybersecurity and data-flow assessment
Identify the information and systems your service depends on
Office and field teams often use several tools to complete one job.
We map an agreed workflow and identify where customer information, access permissions, and operational dependencies need attention, with priorities suited to your team and service model.
What we cover
- 01
Workflow scope
Selected enquiries, quotes, appointments, visits, photos, invoices, and follow-up records.
- 02
System inventory
Scheduling, email, phone, file sharing, payment, accounting, and contractor applications.
- 03
Information sensitivity
Addresses, occupancy notes, access instructions, household photos, and customer communications.
- 04
Ownership mapping
Office, technician, subcontractor, franchise, platform-provider, and support responsibilities.
- 05
Dependency review
Identity, mobile connectivity, hosting, integrations, and information needed during disruption.
- 06
Improvement planning
Findings with owners, priorities, prerequisites, and practical acceptance evidence.
04Office, technician, contractor, and franchise access
Give each person the access their current work requires
An account labelled technician or manager may still have broad access to notes, customer records, schedules, or financial settings. We review actual permissions in selected platforms and verify the effects of approved changes with representative test users.
05Technician mobile and office device security
Reduce exposure when devices travel between jobs
06Booking, customer portal, and integration security
Protect the digital routes into appointments and customer records
Booking pages and service applications connect customers, dispatchers, technicians, payment providers, and marketing tools. We assess selected applications and interfaces using synthetic jobs and test identities, focusing on unauthorised access and actions across those relationships.
07Invoice, payment-link, and customer-communication security
Make payment changes and customer messages easier to verify
An attacker who controls an office mailbox or service-platform account may exploit a legitimate job conversation.
We review the accounts and approval steps behind quotes, invoices, payment links, and changes to bank or payout information.
What we cover
08Household notes, photos, and access-information protection
Limit sensitive home information to legitimate service needs
Entry instructions, occupancy patterns, photographs, alarm details, and household notes can create risks beyond ordinary contact information. We review how selected records are collected, shared, retained, and removed, including copies outside the main service platform.
- 01Collection needsWhich household details the authorised job needs, and who approves collecting them.
- 02Record placementNotes, forms, attachments, photographs, messages, and integrations holding sensitive information.
- 03Need-based accessTechnician, office, contractor, branch, and historical-job visibility.
- 04Sharing routesExports, customer links, personal messaging, forwarded files, and downloaded copies.
- 05Retention and closureApproved review dates, job completion, contract end, obsolete instructions, and deletion limits.
- 06Exposure responseEscalation when sensitive notes, home-access information, or images may have been disclosed.
09 · Smart-home installation and account-handover security
Leave the right people in control after an installation or repair
Where your service includes connected equipment, installer accounts and temporary setup arrangements can persist beyond the visit.
We review the agreed digital handover process for supported devices, focusing on ownership, permissions, documentation, and removal of unnecessary installer access.
What we cover
10Service continuity and incident-response preparation
Prepare office and field teams for disrupted systems
Across the home-service journey
Security priorities across the home-service journey
Protect the handovers between office, crew, and customer. Each stage links to the service on this page that addresses it.
References reviewed October 2026Priorities for assessment, not legal, payment-compliance or trade advice. Platform features depend on the vendor, plan and account, and payment scope is confirmed with your acquirer and advisers.
11Hire a dedicated home services cybersecurity engineer
Hire a Dedicated Cybersecurity Engineer
Add practical security support to your service operation. Agree a profile around your platforms, office tools, and field workflows; a dedicated engineer can coordinate selected improvements while your business controls customer commitments, personnel decisions, and trade work.
01Accounts and devices
- Review agreed roles, authentication, and contractor access
- Support approved device and configuration improvements
- Maintain onboarding, offboarding, and loss-response checklists
02Applications and workflows
- Support authorised booking and portal assessments
- Coordinate payment, photo, and sensitive-note controls
- Track technical findings and agreed retest evidence
03Delivery and accountability
- Agree duties, hours, locations, access, and reporting
- Confirm relevant skills and specialist escalation needs
- Define acceptance checks, supplier coordination, and handover
Onsite trade work, household access, continuous monitoring, and emergency response require separate arrangements.
12Frequently asked questions
Frequently asked questions
Showing 19 of 19 questions
The proposed scope includes repair, maintenance, installation, cleaning, pest control, recurring services, franchises, and marketplaces. The engagement depends on your systems, service model, and verified delivery capability.
Yes. A scheduling platform, office mailbox setup, technician device group, payment workflow, or customer portal can provide a manageable starting point with defined deliverables.
Discuss the technical profile, responsibilities, hours, reporting, and support needs. Availability and relevant experience must be confirmed before commitment.
Approved documentation, configurations, code, and test environments may be suitable. Agree access locations, personnel, customer information, contracts, and evidence handling. Physical visits and device work require separate arrangements.
An authorised review can examine your actual configuration and supported controls. Features depend on vendor, plan, version, and permissions. Mentioning a platform does not imply a Nestack partnership or certification.
No. Check actual access to notes, forms, attachments, history, schedules, and customer databases. Some settings expose information beyond the apparent role boundary, so verify changes with representative test users.
It is one useful control, alongside appropriate permissions, recovery protection, device security, and staff procedures. Platforms support different methods and settings; no method eliminates every account-compromise risk.
Yes, within an agreed ownership and privacy policy. Separate work-data protection from personal-device control. Whole-phone wiping or monitoring is not assumed and requires appropriate authority and safeguards.
Not necessarily. Downloads, screenshots, personal backups, forwarded messages, and offline copies may remain. Review those routes and define owner-approved handling and closure steps.
Review collection, placement, access, sharing, and retention. Limit information to legitimate service needs where supported. Physical code changes require an authorised property owner or responsible service provider.
Routine assessment uses synthetic jobs, test accounts, and agreed environments. Real reassignment, cancellation, messaging, payment, or home-access actions require separate explicit authorisation.
Controls can reduce exposure but cannot guarantee prevention. Independently verify changed bank or payment instructions through a trusted second channel; a familiar email thread alone is insufficient evidence.
No. Scope depends on the payment architecture and merchant responsibilities. PCI SSC FAQ 1588 distinguishes embedded forms from redirects and fully outsourced payment links for one script-related eligibility condition, not every PCI obligation. Confirm scope with your acquirer.
Yes, within scope. Assess branch, central-office, contractor, support, and administrator permissions, including temporary access, shared records, project changes, and offboarding.
An agreed review can examine account ownership, installer access, recovery contacts, linked services, and manufacturer-specific transfer procedures. It does not authorise live camera viewing, unlocking, alarm changes, or resets.
No. Trade licensing, technical installation quality, background checks, safeguarding, physical access, and emergency response require their own responsible people and procedures.
No such coverage is assumed. Agree operational hours, responders, escalation, supplier support, and contractual responsibilities before relying on an ongoing service.
Users, branches, devices, platforms, integrations, sensitive information, testing depth, and access restrictions shape the proposal. Agree deliverables and acceptance criteria after discovery.
Describe your business, broad tools, concern, and engagement preference. Do not submit customer addresses, entry codes, household photos, card details, credentials, or incident evidence through the public form.
Contact and scoping call
Discuss your home-service
security priorities.
Tell us where your team needs support: office accounts, technician access, devices, booking applications, payment workflows, household information, smart-home handovers, recovery, or a dedicated engineer.
Loading open times…
Open times
Select an available date above to view open 45-minute times from our calendar.