
Medical device cybersecurity
Medical Device Cybersecurity
Expertise for Your Team
Build security evidence across your device lifecycle. Connect product architecture, software components, security testing, connected services, and postmarket response, with practical improvements that fit your device, intended environment, quality processes, and accountable engineering teams.
A device may depend on embedded software, mobile applications, cloud services, hospital interfaces, update systems, and remote support.
A weakness outside the physical device can still expose sensitive information, alter a trusted exchange, or affect availability, so product security must follow those relationships throughout development and support.
Nestack helps your teams assess defined risks, implement approved controls, and produce traceable technical evidence. We work with product engineering, quality, regulatory, and clinical specialists so security findings enter the decisions and change processes they own.
Three ways to work with Nestack
- 01
Focused assessment
Review a device architecture, component inventory, connected service, test scope, or update pathway.
- 02
Dedicated security engineer
Add agreed technical capacity with defined responsibilities, hours, supervision, and reporting.
- 03
Lifecycle improvement
Coordinate remediation, release evidence, supplier actions, and vulnerability-management readiness.
Manufacturer, quality, regulatory, clinical, and healthcare-operator responsibilities remain with their accountable owners.
02Who we help
Support aligned with your product and lifecycle role
For medical-device manufacturers, software-device developers, connected diagnostics businesses, and specialist product suppliers worldwide.
Integrate security requirements, testing, updates, and evidence into defined product programmes.
Assess applications, backend services, device relationships, and clinical-data interfaces within confirmed product scope.
Review connected instruments, companion software, result exchanges, service access, and support dependencies.
Prepare component evidence, controlled deliverables, vulnerability information, and handovers for device manufacturers.
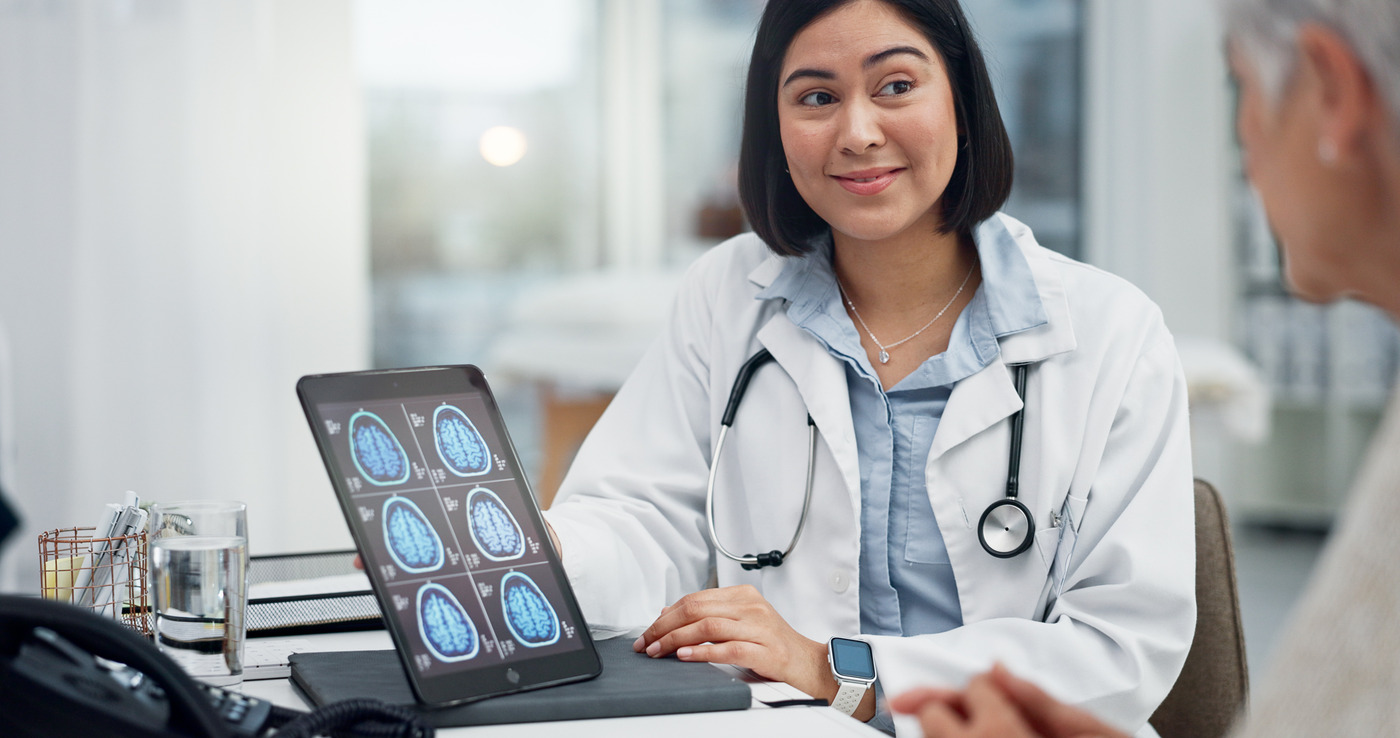
Work alongside your product, quality, and clinical specialists
This is a manufacturer and product-lifecycle offering, agreed in scope, test environment, and safe working methods before work starts.
03Device security scope and threat modelling
Connect attack paths with the device's intended environment
We develop an agreed view of the device system, its users, external dependencies, and trust boundaries.
Technical findings are then connected to the manufacturer's risk process so their significance can be considered alongside intended use, essential functions, and potential patient impact.
What we cover
- 01
Product boundary
Device variants, software releases, accessories, applications, cloud services and supporting infrastructure, identified.
- 02
Intended environment
Approved users, connectivity, deployment assumptions, maintenance roles and foreseeable misuse inputs, recorded.
- 03
Trust relationships
Interfaces, identities, data movement, commands, updates and privileged service pathways, mapped.
- 04
Threat scenarios
Selected misuse routes, compromised dependencies, access failures and availability threats, examined.
- 05
Risk-process links
Security findings connected with manufacturer-owned safety analysis, control decisions and residual-risk review.
- 06
Evidence planning
Assumptions, requirements, verification needs, owners and review triggers defined as the product changes.
04Secure architecture and product control implementation
Make security controls fit the device and its users
We support agreed security requirements in device software and related systems, considering operational constraints and the consequences of control failure. The aim is a reviewable implementation with explicit assumptions and evidence, not a collection of features disconnected from the product's risk analysis.
05Software component, SBOM, and build security
Know what is in a release and how it reached the product
Component visibility is valuable when it connects to the actual released device software and its supporting services. We help review component records, build dependencies, and supplier handovers so a vulnerability notice can be investigated against identifiable product versions and accountable owners.
- 01Release inventorySoftware components, versions, dependencies, suppliers and relevant identifiers, associated with agreed releases.
- 02SBOM qualityCompleteness assumptions, machine-readable output, generation methods and update responsibilities.
- 03Supplier evidenceSupport terms, vulnerability contacts, component updates and missing or inconsistent information.
- 04Build integritySource access, dependency sources, build identities, artefact handling and release approval.
- 05Exposure analysisAdvisories connected to included components, configuration, reachability and product-specific assessment needs.
- 06Change trackingDifferences between releases, unresolved findings, remediation decisions and affected-version records, preserved.
06Controlled device and software security verification
Produce reproducible findings within a safe test boundary
We define security tests around agreed requirements, interfaces, and representative configurations. Testing uses isolated environments and sample data so results can support remediation without exposing patients or disrupting clinical operations, and findings include their conditions and practical limits.
07Device cloud, companion application, and API security
Preserve boundaries between devices, users, and clinical organisations
08Secure updates, service access, and recovery design
Keep product maintenance under controlled authority
09Postmarket vulnerability and support readiness
Turn incoming reports into accountable product decisions
Vulnerability information can arrive from researchers, suppliers, customers, or internal testing.
We help establish a technical handling process that connects each report to affected versions, investigation evidence, remediation options, and the manufacturer-owned quality and regulatory decisions that follow.
What we cover
10 · Cybersecurity evidence and quality-process support
Make technical work reviewable across development and support
Useful security evidence shows which product and version were assessed, what was decided, what was tested, and what remains unresolved.
We help organise selected technical artefacts so your quality and regulatory teams can review them within the product's established documentation and change processes.
What we cover
Across the device lifecycle
Medical device security priorities across the lifecycle
Maintain evidence as the product and its environment change. Each stage links to the service on this page that addresses it.
References reviewed October 2026Priorities for assessment, not legal or regulatory advice. FDA, EU, IMDRF, TGA and IEC material informs scope rather than setting universal obligations, and qualified regulatory owners confirm which requirements and editions apply. Nestack does not claim regulatory clearance, conformity assessment, certification or authority to approve device release.
11Hire a dedicated medical device cybersecurity engineer
Hire a Dedicated Cybersecurity Engineer
Add product-security capacity within your quality processes. An agreed engineer can support a defined backlog alongside product, quality, regulatory, and clinical specialists; competence, supervision, access, availability, and specialist testing resources are confirmed before engagement.
01Assess and specify
- Map device-system boundaries and assumptions
- Develop scoped threat models and security requirements
- Review component and connected-service evidence
02Implement and verify
- Support approved software and configuration changes
- Run controlled tests on authorised environments
- Record findings, remediation and retest evidence
03Coordinate and maintain
- Track release evidence and supplier actions
- Support vulnerability triage and maintenance planning
- Report unresolved risks and required specialist decisions
Clinical validation, safety acceptance, regulatory interpretation, independent certification, and return-to-use decisions require their own accountable specialists.
12Frequently asked questions
Frequently asked questions
Showing 19 of 19 questions
This page focuses on manufacturers, product developers, and their suppliers. Healthcare operators may participate in deployment and support coordination, but hospital-wide IT security requires a separate engagement.
Selected software, cloud, mobile, and interface work can be scoped after the product boundary and intended use are confirmed. Qualified regulatory owners determine whether a function is a medical device and which requirements apply.
The agreed scope may include embedded software, applications, backend services, interfaces, updates, provisioning, and support systems. The physical device alone may not contain every relevant trust relationship.
As of 25 October 2026, FDA's final guidance issued 3 February 2026 covers quality management system considerations and premarket cybersecurity content. It supersedes the June 2025 guidance. Regulatory owners confirm applicability and any subsequent changes.
No. Its statutory duties apply within the defined cyber-device and submission scope. FDA's broader recommendations address devices with cybersecurity risk; an actual internet connection alone is not a complete applicability test.
No. FDA's QMSR became effective on 2 February 2026. Its incorporation of ISO 13485:2016 does not mean an ISO certificate establishes FDA acceptance. Quality and regulatory owners determine the relevant obligations.
No. We can support agreed technical work and evidence. Regulatory authorisation, conformity assessment, clinical evaluation, and manufacturer declarations require their respective processes and accountable parties.
Yes, where relevant and agreed. It addresses health-software security lifecycle activities. Scope, applicable edition, interpretation material, and required evidence must be confirmed; using it does not establish clinical validation or automatic device approval.
It helps identify software components associated with a release and supports vulnerability investigation. Completeness, accuracy, updates, and supplier inputs matter. An SBOM does not prove that the device is safe or free of vulnerabilities.
No patient-connected testing is assumed. Work uses authorised isolated devices, representative configurations, synthetic data, and test credentials. Any different arrangement requires a separately defined specialist process and appropriate approvals.
No. Security testing provides evidence within a defined scope. Clinical performance, safety, usability, regression, and quality-system validation require their own activities and acceptance criteria.
Yes, within approved scope and environments. Tests examine device, user, organisation, record, and function boundaries without changing live clinical data, issuing therapy commands, or accessing unapproved patient information.
Deployment must follow the manufacturer's approved design and change process, with operator coordination where needed. Testing, safety and regulatory impact, recovery, and local acceptance must be considered before choosing an update approach.
We can support scoped technical triage, affected-version mapping, reproduction, and mitigation evidence. The manufacturer owns patient-risk assessment, regulatory reporting, field actions, communications, and release decisions.
We can assess technical dependencies and support-transition options with the manufacturer and operators. Device age alone does not determine cybersecurity legacy status. Compensating measures and retirement decisions require product-specific evaluation.
No. The CRA exclusion concerns products to which the MDR or IVDR applies. Other software or digital products supplied by the same business need their own scope assessment; healthcare use alone is not a blanket exemption.
Some documentation, software, and isolated-environment work can be remote under approved contracts, locations, personnel, and access. Patient data, controlled devices, and physical testing may require different arrangements or qualified onsite participation.
Coverage, availability, escalation, and response commitments must be explicitly agreed. No service can establish complete vulnerability absence, guarantee clinical availability, or replace manufacturer responsibilities throughout product support.
Provide a non-sensitive product description, lifecycle stage, intended markets, system boundary, and main concern. Do not send patient records, production credentials, signing keys, or confidential design files before an approved exchange is established.
Contact and scoping call
Discuss your medical device
security requirements.
Tell us which product, software release, connected service, or lifecycle activity needs support. We can define the technical scope, responsible specialists, safe test environment, and evidence expected from an engagement.
Loading open times…
Open times
Select an available date above to view open 45-minute times from our calendar.