
Mining cybersecurity
Mining Cybersecurity
Expertise for Your Team
Protect sensitive exploration and operational information. Strengthen the security of the systems connecting your people, sites, and suppliers. Turn security findings into a practical improvement plan with clear ownership and operational coordination.
Mining businesses connect corporate applications, exploration data, remote-site services, technology vendors, and operational systems.
Those connections help teams work, but they also create access, information-handling, and recovery responsibilities that can span several owners.
Nestack helps your IT, security, geoscience, and site teams identify priorities and carry forward agreed improvements. The engagement starts by establishing which systems are in scope, who controls them, and which activities require specialist or operational approval. We define the deliverables and responsibilities before technical work begins.
Three ways to work with Nestack
- 01
Dedicated cybersecurity engineer
Add a consistent resource for an agreed security work plan, schedule, and reporting rhythm, working alongside your teams and coordinating specialist input where required.
- 02
Scoped security assessment
Examine a defined site IT environment, application, access arrangement, or security concern, and receive evidence-based findings and an agreed approach to verification.
- 03
Ongoing security support
Maintain recurring reviews, risk tracking, evidence, remediation coordination, and reporting as sites, suppliers, and systems change.
The scope distinguishes enterprise IT, site IT, and operational technology. A general security engagement does not automatically include testing or changing production equipment.
02Who we help
Security support for the businesses behind mining operations
Mining organizations have different information, systems, and operating responsibilities. We shape the work around your environment and the access your organization can authorize.
Review corporate and site IT, supplier connectivity, identity, business applications, and recovery dependencies. Coordinate any work affecting operational environments with the designated site and equipment owners.
Review access to geological models, survey information, drill-hole and assay data, project documents, and commercially sensitive material. Assess collaboration, export permissions, laboratory interfaces, and relevant applications according to actual information classification.
Review support access, workforce devices, software interfaces, and customer-assurance evidence. Establish how your people and tools connect to customer environments, and how access is approved, monitored, and removed.
Assess customer-owned applications, portals, reporting services, and integrations supporting planning, logistics, maintenance, or workforce administration. Product teams receive validated findings and remediation guidance within an authorized scope.
Work with your existing teams
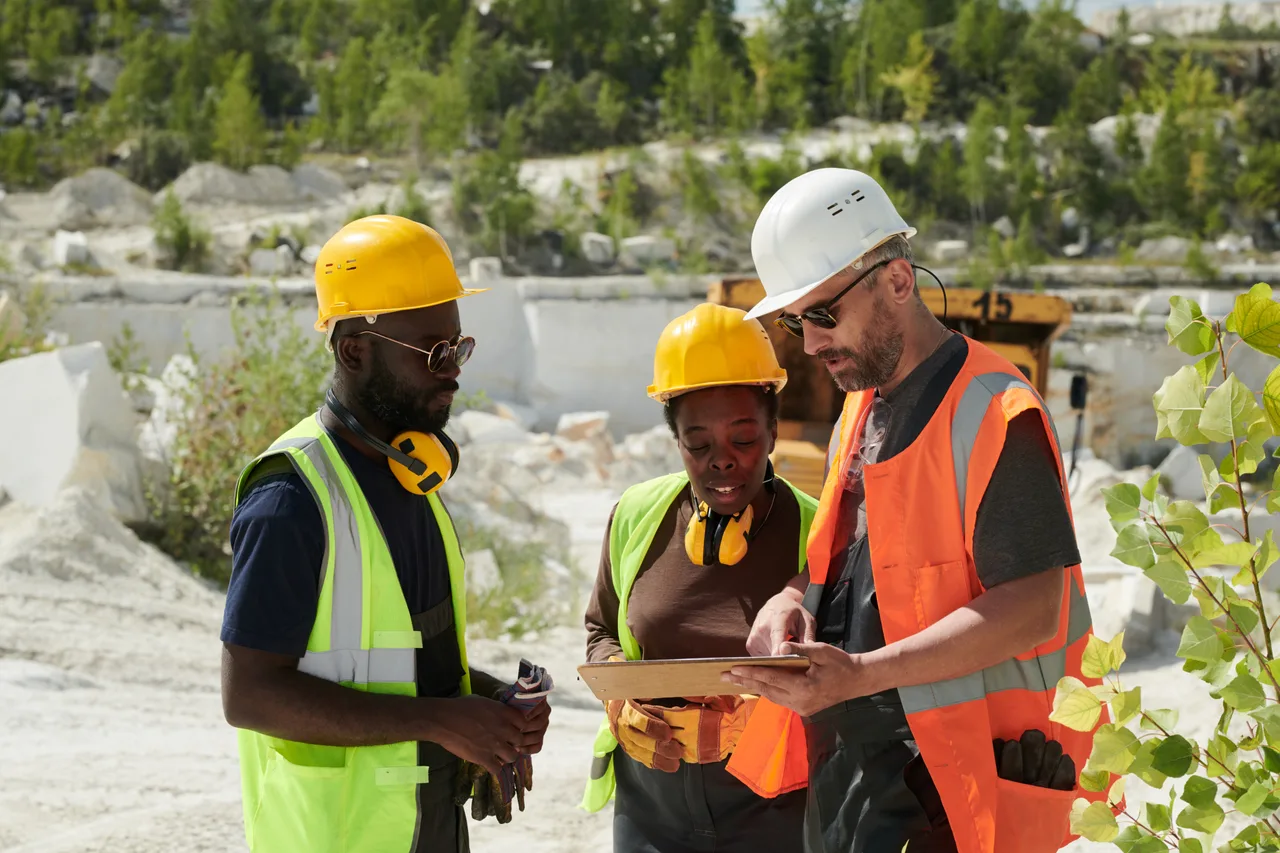
We coordinate with internal IT, OT specialists, geoscience teams, security operations providers, engineering owners, and equipment vendors. The mine operator retains authority over operational changes and safe operating decisions.
03Mining cybersecurity risk assessment
Connect security findings with business and site dependencies
Restricted exploration information, a corporate identity service, and a vendor connection to a site environment have different owners and consequences if something goes wrong. A useful assessment identifies those differences before prioritizing action.
Nestack can review an agreed information and technology environment, examine available evidence, and document risks, existing safeguards, and practical improvements. Site and business owners help establish the operational context.
Assessment scope
- 01
Systems and information flows
Identify corporate applications, exploration platforms, approved site IT, interfaces, and information stores within scope.
- 02
Identities and administration
Review employees, contractors, OEM support, administrators, service accounts, and integration credentials.
- 03
Existing safeguards
Examine evidence for configurations, access controls, vulnerability management, logging, backups, and incident arrangements.
- 04
Business and site dependencies
Map how losing an in-scope service could affect other teams or systems, including separately owned operational environments.
- 05
Ownership and prioritization
Identify accountable owners, evidence gaps, practical actions, specialist needs, and risk decisions requiring approval.
01Former consultant retains geological-data export access
Evidence to examine:Project membership and approved responsibilities
Possible consequence:Unnecessary access to restricted project information
Recommended action:Confirm need and remove or renew access explicitly
Proposed owner:Data/project owner
02Supplier support uses an unattributed shared account
Evidence to examine:Account inventory and support-access records
Possible consequence:Weak accountability for remote activity
Recommended action:Agree named access, approvals, duration and logging
Proposed owner:IT/vendor owner
03A documented connection bypasses the intended site boundary
Evidence to examine:Owner-provided architecture and configurations
Possible consequence:Broader access than the approved design permits
Recommended action:Validate exposure with specialists and plan an approved change
Proposed owner:Site network owner
04Critical business records lack restore-test evidence
Evidence to examine:Backup scope and restoration records
Possible consequence:Uncertain recovery capability during disruption
Recommended action:Plan and perform an authorized IT restore test
Proposed owner:IT recovery owner
05An assistant can retrieve an overshared confidential report
Evidence to examine:Permissions and approved retrieval test results
Possible consequence:Sensitive material reaches unintended users
Recommended action:Correct source access and retest retrieval boundaries
Proposed owner:Information owner
These entries are fictional examples of report content, not findings about a Nestack customer. Actual impact and priority depend on the assessed environment.
04Mining application, API, and data security
Review the boundaries around your applications and mining information
We assess authorized customer-owned applications and interfaces. Reviewing a customer tenant or integration is distinct from testing a SaaS vendor's underlying platform, which needs the vendor's authorization.
05Cloud, remote-site IT, and boundary security
Review the connections between corporate and site environments
06Identity, privileged, and contractor access
Make every important access path accountable
We review roles, privileges, approval practices and access lifecycles across an agreed set of systems and information.
07Ransomware and recovery readiness
Prepare to restore information and coordinate recovery decisions
08Security governance and customer assurance
Demonstrate security practices with evidence and clear ownership
Mining customers and project owners may ask suppliers how they manage risk, remote access, sensitive information, incidents, and recovery. Useful assurance connects those questions with the actual environment and evidence.
Nestack can support defined gap reviews, evidence organization, and remediation coordination for the requirements relevant to your business or customer engagement.
What the engagement can cover
09OEM, supplier, and third-party security
Review the access and dependencies introduced by your suppliers
We assess defined supplier relationships and support practical conditions for access, evidence, incident coordination and exit.
- 01Supplier classificationThe service, information, access, and business or site dependency involved.
- 02Evidence reviewRelevant assurance documentation, its scope, age, limitations and open questions.
- 03Remote-access conditionsApproved users and routes, permissions, support purpose, duration, logging and termination.
- 04Incident coordinationContacts, escalation, notification responsibilities and dependencies affecting response.
- 05Continuity and exitInformation availability, transition, support dependencies, and access removal or transfer.
- 06Change and reassessmentWhen systems, integrations, services or responsibilities change.
10 · Mining AI and agent security
Control the information and actions available to mining assistants
AI tools may help search geological reports, summarize maintenance documents, prepare procurement material, or answer questions using internal procedures. Their security depends on source permissions, connected systems, information handling, and the authority given to their outputs or tools.
Nestack can review a defined AI workflow and evaluate agreed information and action boundaries. The review does not validate resource estimates, engineering conclusions, autonomous equipment, or operational safety.
What the review can cover
Across connected mining
Security priorities for connected mining
Eight areas to examine as sites, suppliers, and systems evolve. Each is an assessment priority rather than a new legal requirement, with the service that addresses it and a published reference.
References reviewed October 2026Priorities for assessment, not legal advice or claims that every mine has the same exposure. Contractual, site and jurisdiction-specific obligations are identified during scoping.
11Hire a dedicated mining cybersecurity engineer
Hire a Dedicated Cybersecurity Engineer
One consistent engineer who carries agreed security work forward across your business, site IT and supplier stakeholders, working remotely from India through approved arrangements.
01The engineer owns
- Security backlog and risk register
- Contractor, supplier and privileged-access reviews
- Cloud, application, identity and data changes
- Supplier-assurance evidence and questionnaires
- Preparedness exercises and escalation
- Reporting on progress, risks and blockers
02You decide
- Information classification and legitimate access
- Production access and change approvals
- Business-risk acceptance and investment
- Engineering, safety and operational restart
03Agreed up front
- Role, supervision and schedule
- Timezone overlap and access routes
- Deliverables, reporting and verification
- Leave cover and handover
- Specialist, on-site and out-of-hours needs
Full-time means an agreed working schedule. A dedicated engineer is not a continuously staffed SOC, emergency-response team or OT specialist service; site and equipment work may need local teams.
12Frequently asked questions
Frequently asked questions
Showing 19 of 19 questions
Yes. Review the proposed role, relevant experience, and technical approach before confirming the assignment. Availability, supervision, schedule, and commercial terms are agreed before work begins.
Yes. The scope defines assessment, implementation, approval, verification, and escalation responsibilities. We coordinate the agreed security work without assuming the authority of operational owners or specialist vendors.
Yes. A vendor-access review, sensitive-data permission review, application assessment, or enterprise recovery-readiness exercise can provide a bounded starting point. Findings can inform further work where justified.
Scope can include authorized business applications, cloud services, exploration-data platforms, portals, site IT, and integrations. Each engagement identifies ownership, required expertise, permitted methods, and dependencies. Production-connected systems require additional assessment of impact and authority.
Only within the vendor's applicable authorization and terms. Reviewing permitted customer configurations or a customer-owned integration is different from testing the vendor's infrastructure.
Not by default. Work involving equipment control, ventilation, dewatering, protective systems, or other operational technology requires separately agreed specialist scope, owner approval, and appropriate vendor coordination. General IT testing does not validate functional safety.
Agree systems, methods, operating windows, exclusions, escalation, and stop conditions. Use evidence review and suitable test environments where appropriate. Intrusive activity requires specific authorization and impact review; no assessment is represented as having zero operational risk.
Document the constraint and coordinate an owner-approved path with suitable specialists. Options may include restricted access, boundary controls, monitoring, or a planned replacement. Compensating measures must be evaluated for the actual environment rather than treated as a permanent universal substitute.
Yes, within an agreed scope. Examine approved users, tools, routes, permissions, duration, logging, and revocation. Changes affecting operational support require the appropriate owner's approval and coordination with the vendor.
The designated mine operator, system owners, and relevant engineering or safety specialists. A restored file, completed IT recovery test, or cybersecurity retest is not authorization to restart equipment or resume production.
Where suitable, work can use client-controlled environments and restrictions on local copies. Delivery locations, remote viewing, logs, storage, and contractual or legal requirements still need review. Hosting location alone does not determine whether offshore access is permitted.
Establish the restriction before onboarding. Some reviews may use redacted evidence or client-led demonstrations, with limitations stated. Work that cannot be performed within approved arrangements requires an appropriate alternative delivery model.
We can review defined requirements, identify evidence gaps, and coordinate technical improvements. A particular operator's requirements are not universal rules. Buyer acceptance, independent certification, and legal conclusions remain separate decisions.
No. The assignment has an agreed schedule. Continuous monitoring, out-of-hours response, and specialist escalation require an appropriately staffed and separately defined service. The proposal specifies actual coverage.
The proposal identifies both explicitly. An assessment may provide recommendations only, while a wider engagement may include approved implementation and verification. Reports distinguish suggested actions from changes that have been completed and checked.
Emergency availability is not implied by this page or a general engineering assignment. Incident response needs confirmed contacts, authority, coverage, and specialist capability. Use your established incident arrangements during an active event.
AI-assisted work must follow the agreed information-handling rules. Restricted mining information, credentials, and assessment evidence must not be put into unapproved services. Engineers remain responsible for validating findings and respecting access boundaries.
No. Reviewing an assistant's access, disclosure, and action boundaries does not validate resource estimates, engineering recommendations, machinery performance, or operating safety. Those require the appropriate domain expertise and assessment.
Scope, complexity, access restrictions, evidence, expertise, delivery locations, and implementation or retesting affect the proposal. Agree timing, costs, deliverables, outstanding-action handover, evidence retention, and access removal before work starts.
Contact and scoping call
Tell us where you need
mining security support.
Start with your concern and the systems involved: an engineer, remote access, sensitive information, an application, or preparing for disruption.
Loading open times…
Open times
Select an available date above to view open 45-minute times from our calendar.